The Future of API Security
On February 15, 2018, Bernard Harguindeguy of Elastic Beam and I filmed a webcast on The Future of API Security. The webcast can be viewed here.
Read article: The Future of API SecurityNotes on application security, API security, identity, and API management from the field. Articles are also published on Medium. Browse the archive by topic instead — 124 subjects.
On February 15, 2018, Bernard Harguindeguy of Elastic Beam and I filmed a webcast on The Future of API Security. The webcast can be viewed here.
Read article: The Future of API SecurityIt so happened that one day, in a corporate IT department not unlike the one you are familiar with, three IT resources were preparing to design a software system. It doesn’t much matter what the system is or what it is supposed to do, for the results would be more-or-less the same. The assembled…
Read article: The Tale of Thomas, Richard, and Karen — A Software Architecture ParableThis blog post summarizes the details of how to deploy and configure the the Apigee Edge OAuth2 example that I put together. This example will use the OAuth2 Authorization Code Grant and Refresh Token Grant to demonstrate how OAuth2 can be used with Apigee Edge in a real-world application.
Read article: Apigee Edge OAuth2 and Third-Party Identity ProvidersThis post describes the Refresh Token support that was added to the OAuth2 + OIDC Debugger in late 2017. The OAuth2 + OIDC Debugger is a general-purpose testing tool for the OAuth2 and OpenID Connect protocols. It has been tested with many of the leading Identity Providers in the industry.
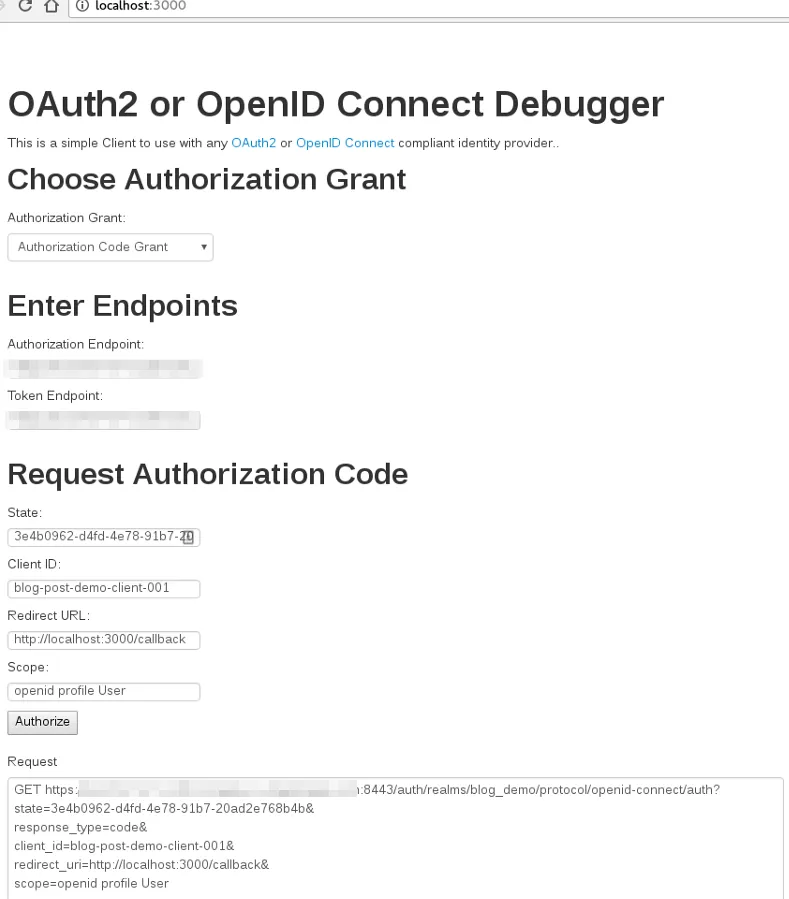
Read article: Refresh Token Support in OAuth2 + OIDC DebuggerI recently finished implementing OAuth2 and OIDC support for Azure Active Directory in my OAuth2 + OIDC Debugger. Previously, we implemented support for Red Hat SSO v7.1 and 3Scale. This post compares the two product’s implementations of these protocols (OAuth2 and OIDC). In particular, it looks at…
Read article: Differences Between Azure Active Directory and Red Hat SSO v7.1This blog post continues demonstrating (and documenting) the use of the OAuth2 + OIDC Debugger with 3Scale API Management and Red Hat SSO. Now, we are going to look at the OAuth2 Resource Owner Password Credential Grant with 3Scale and Red Hat SSO.
Read article: OAuth2 Resource Owner Password Credential Grant with 3Scale and Red Hat SSOThis post demonstrates the OAuth2 Implicit Grant with 3Scale SaaS, APICast Gateway, and Red Hat SSO v7.1. In the last post, we introduced these components and demonstrated a functioning OAuth2 Authorization Code Grant (and OpenID Connect Authorization Code Flow). This is all part of my 3Scale API…
Read article: OAuth2 Implicit Grant with 3Scale and Red Hat SSOThis tutorial builds on the capabilities we explored in the “Red Hat SSO + 3Scale API Management” series and in particular in the first tutorial. In this post, we will:
Read article: OAuth2 Configuration in 3Scale API Management (and APICast) with Red Hat SSOThis post continues our exploration of OAuth2 Authorization Grants with Red Hat SSO v7.1. In previous posts, we looked at:
Read article: Red Hat SSO v7.1 OAuth2 Client Credentials GrantIn this post, we will look at an example of the OAuth2 Resource Owner Password Credential Grant using Red Hat SSO v7.1. In previous posts, I described the Red Hat SSO setup for OpenID Connect authentication and OAuth2. We have also looked at examples of:
Read article: Red Hat SSO v7.1 OAuth2 Resource Owner Password Credential Grant SupportLooking for something specific? Browse all 124 topics.