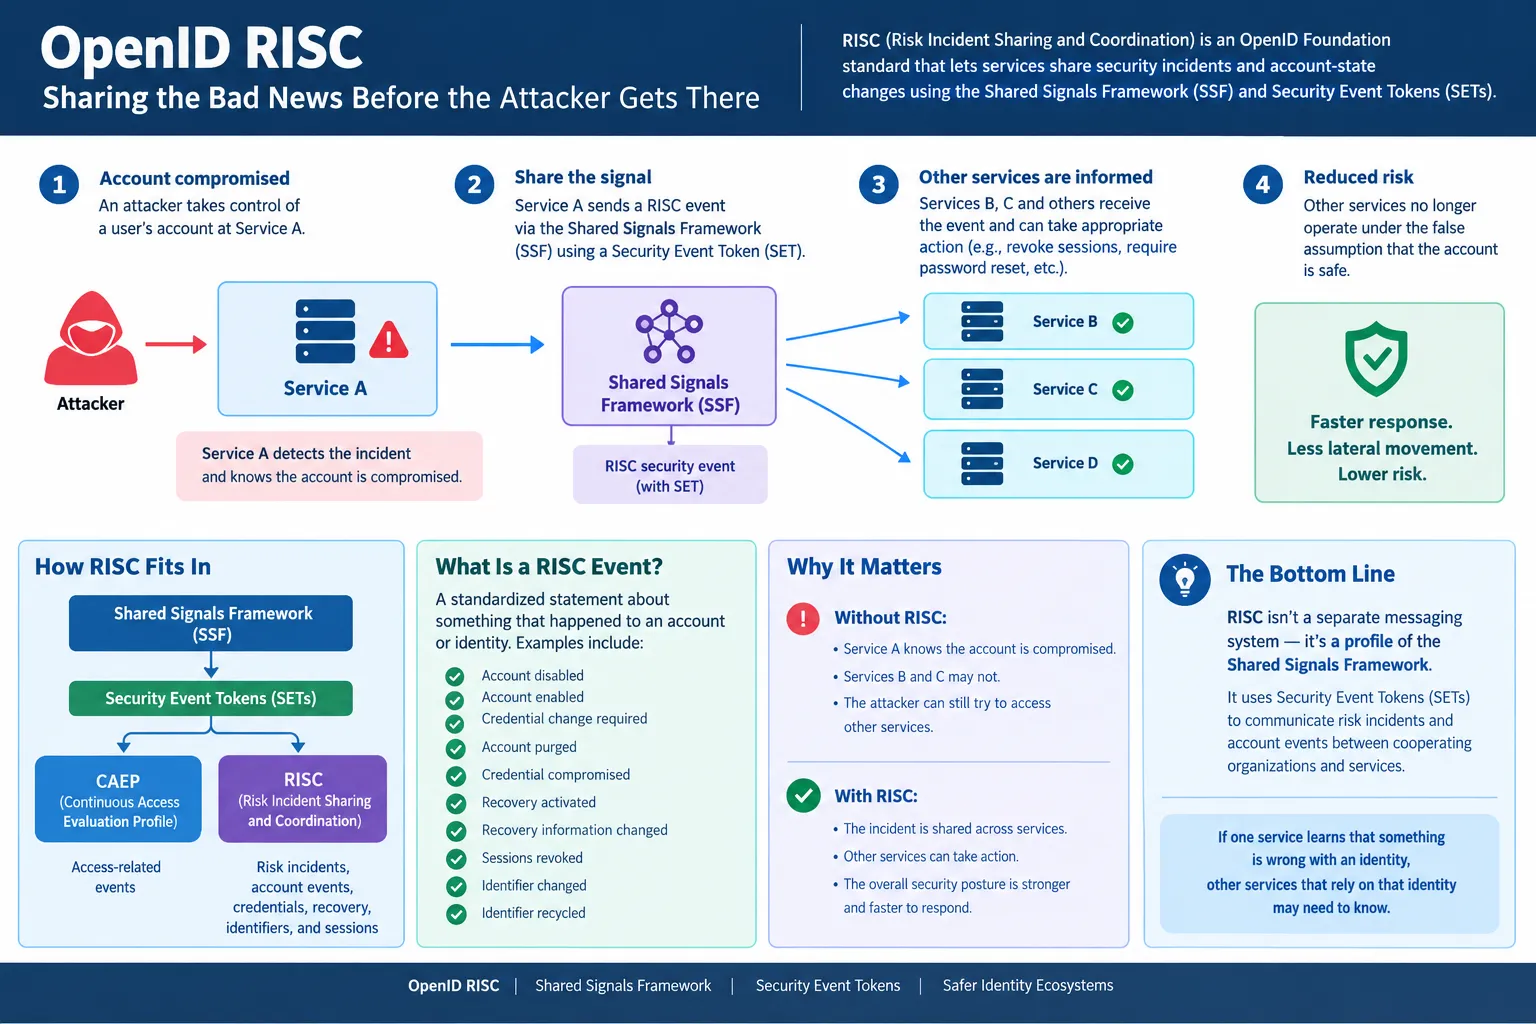
OpenID RISC: Sharing the Bad News Before the Attacker Gets There
In modern identity systems, a compromise at one service can become a compromise at another service.
Read article: OpenID RISC: Sharing the Bad News Before the Attacker Gets There50 articles tagged Identity.
In modern identity systems, a compromise at one service can become a compromise at another service.
Read article: OpenID RISC: Sharing the Bad News Before the Attacker Gets ThereThere is a basic assumption hiding inside many identity architectures in that if someone authenticated successfully, they should continue to have access.
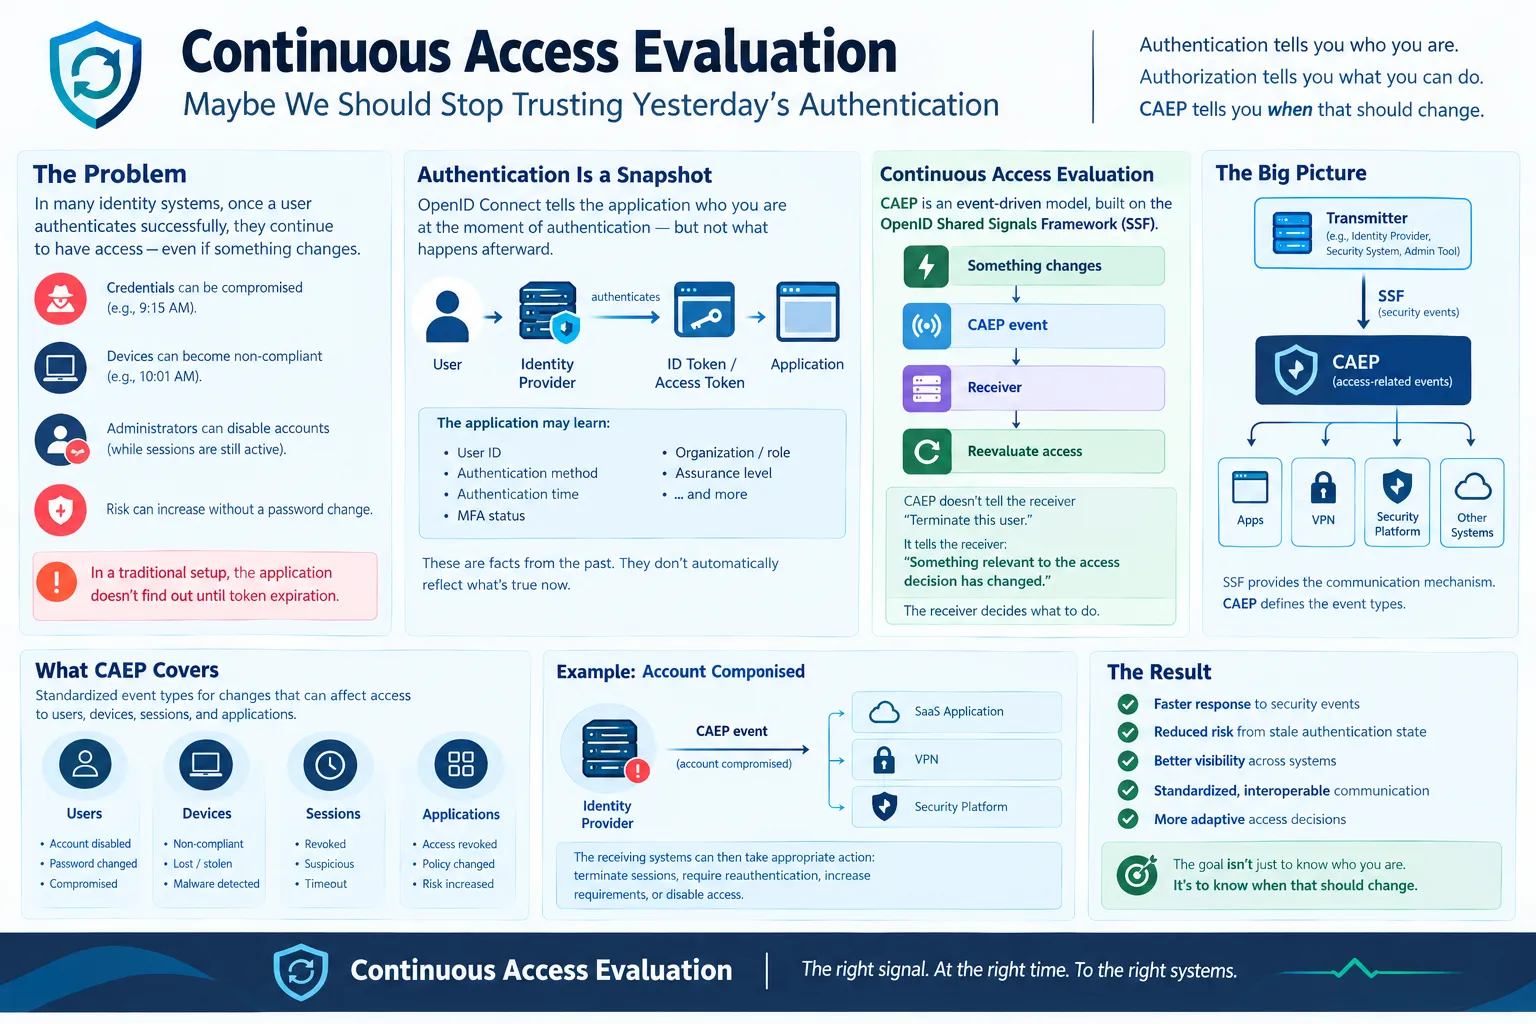
Read article: Continuous Access Evaluation: Maybe We Should Stop Trusting Yesterday’s AuthenticationThere is a fundamental problem with modern identity systems that is easy to overlook.
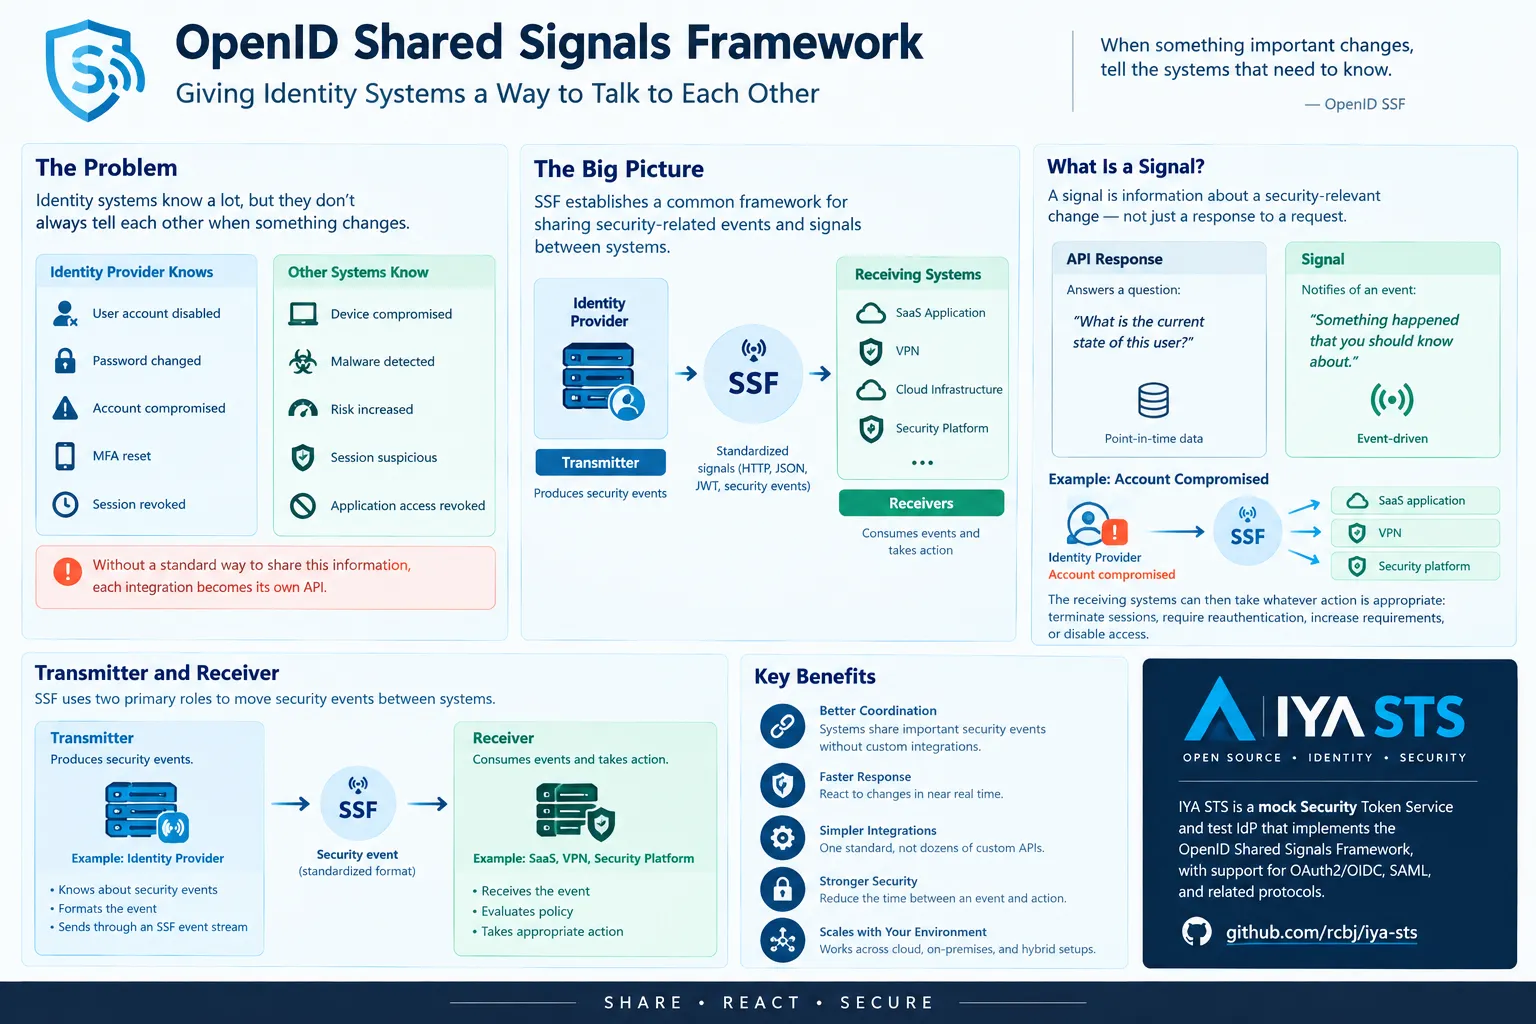
Read article: OpenID Shared Signals Framework: Giving Identity Systems a Way to Talk to Each OtherIdentity systems have a bad habit of starting with a simple question: Who are you?
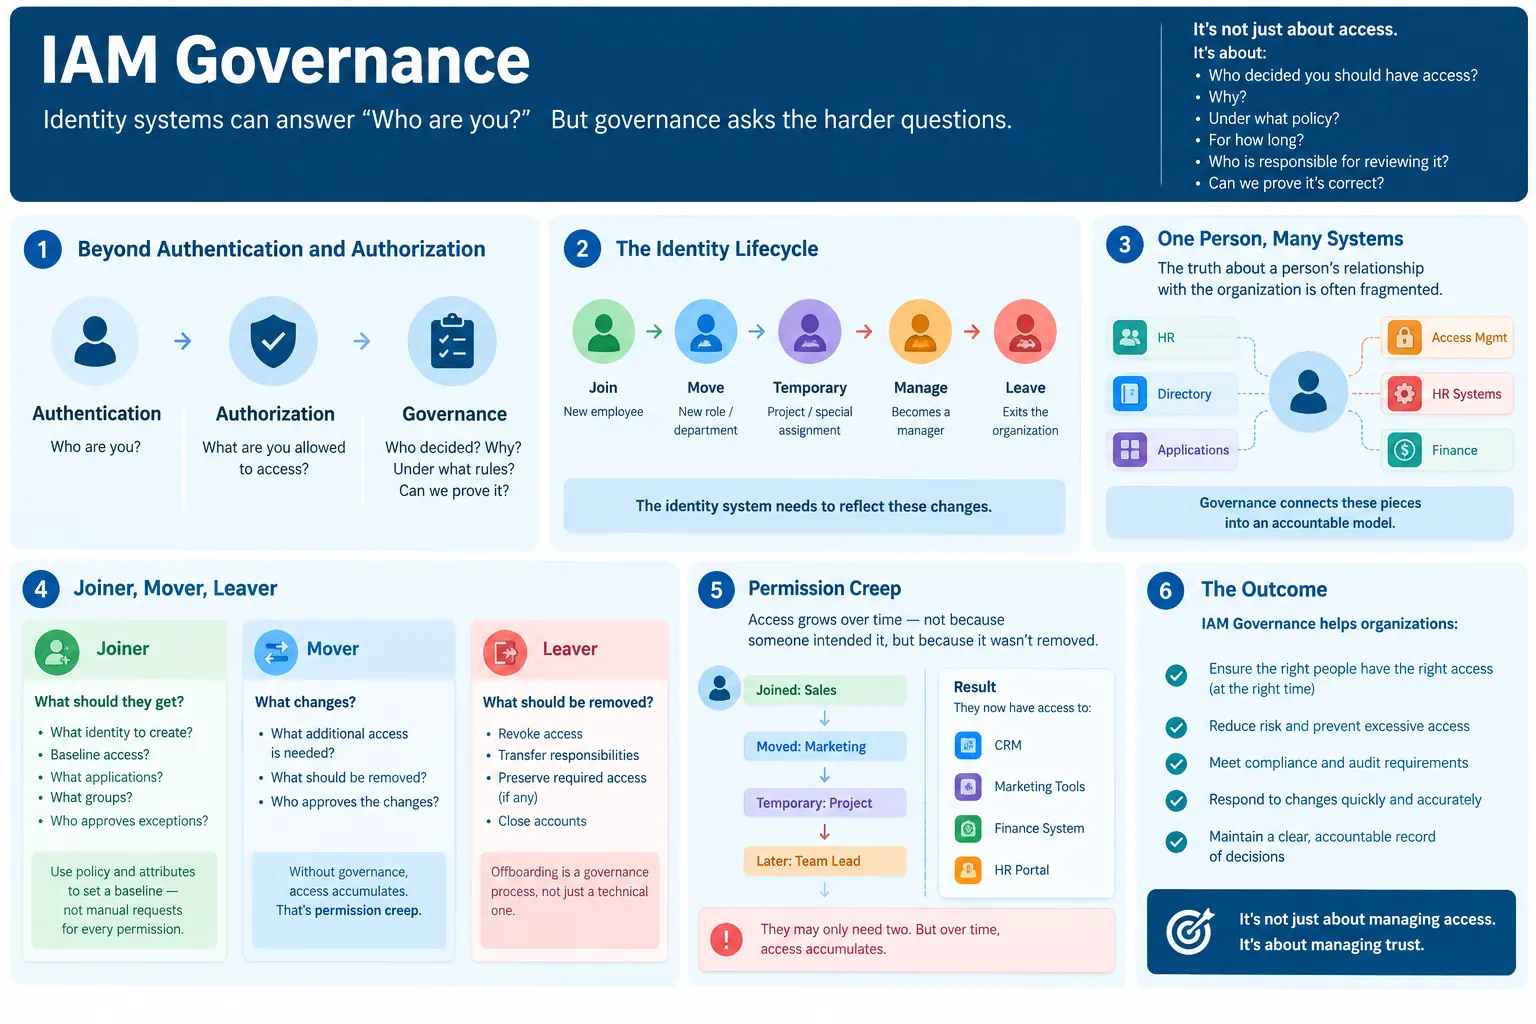
Read article: IAM GovernanceThere is a recurring problem in digital identity: I want to prove something about myself, but, I don’t necessarily want to tell you everything about myself in the process.
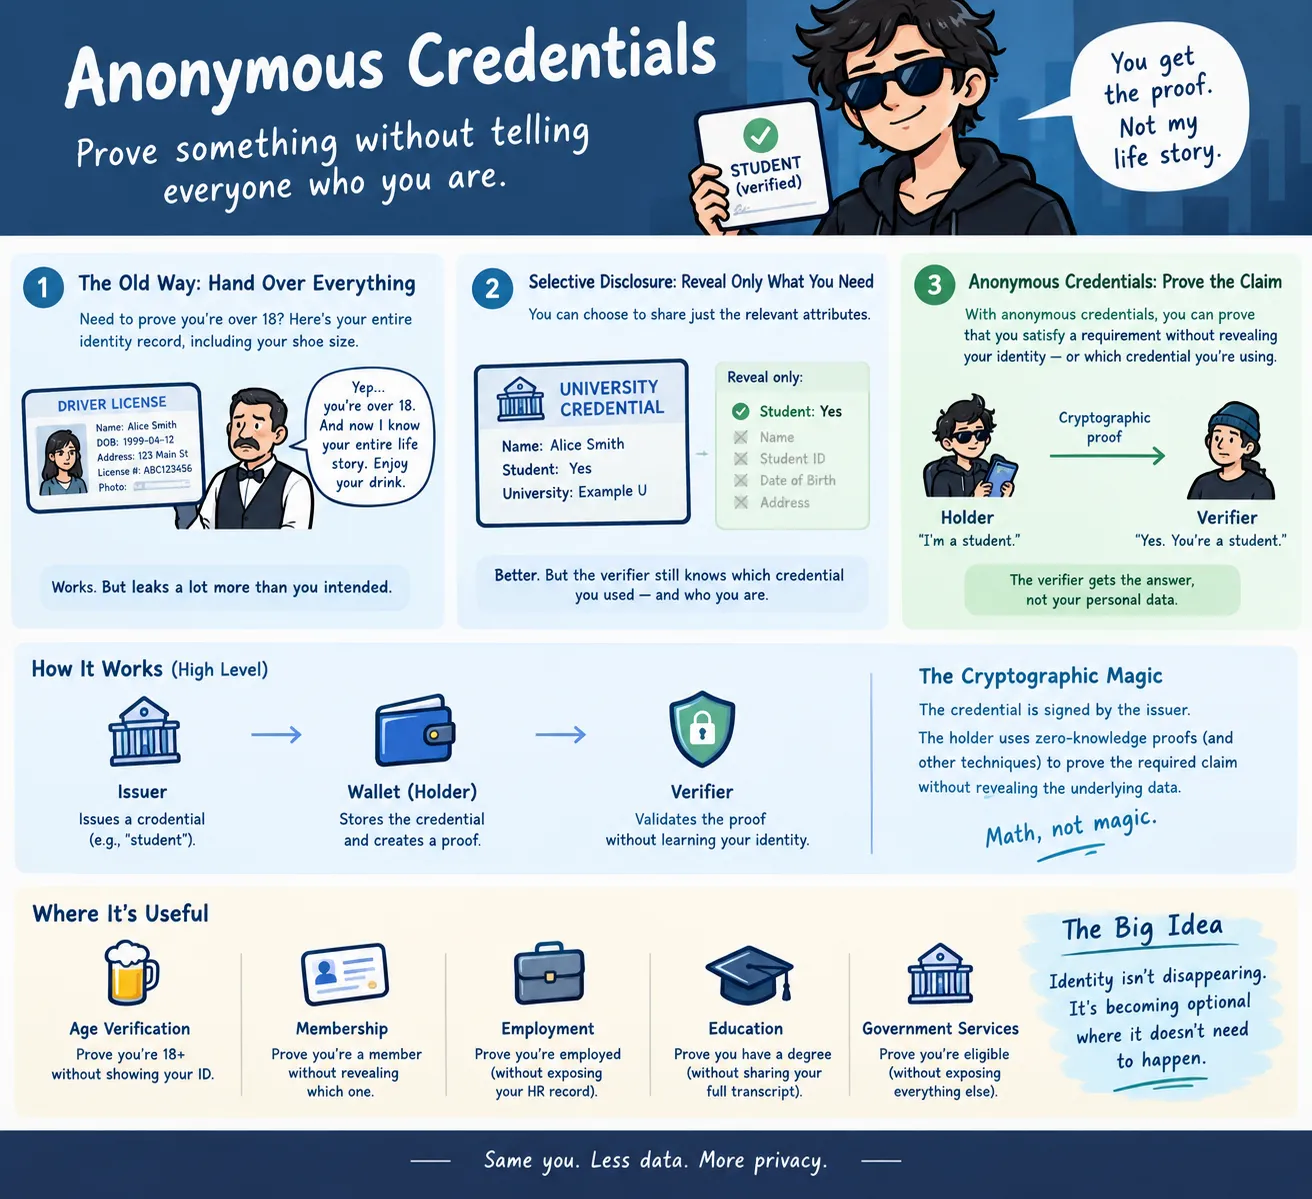
Read article: Anonymous Credentials: Prove Something Without Telling Everyone Who You AreThere is a glamorous side to identity management, if any of this actually constitutes glamorous.
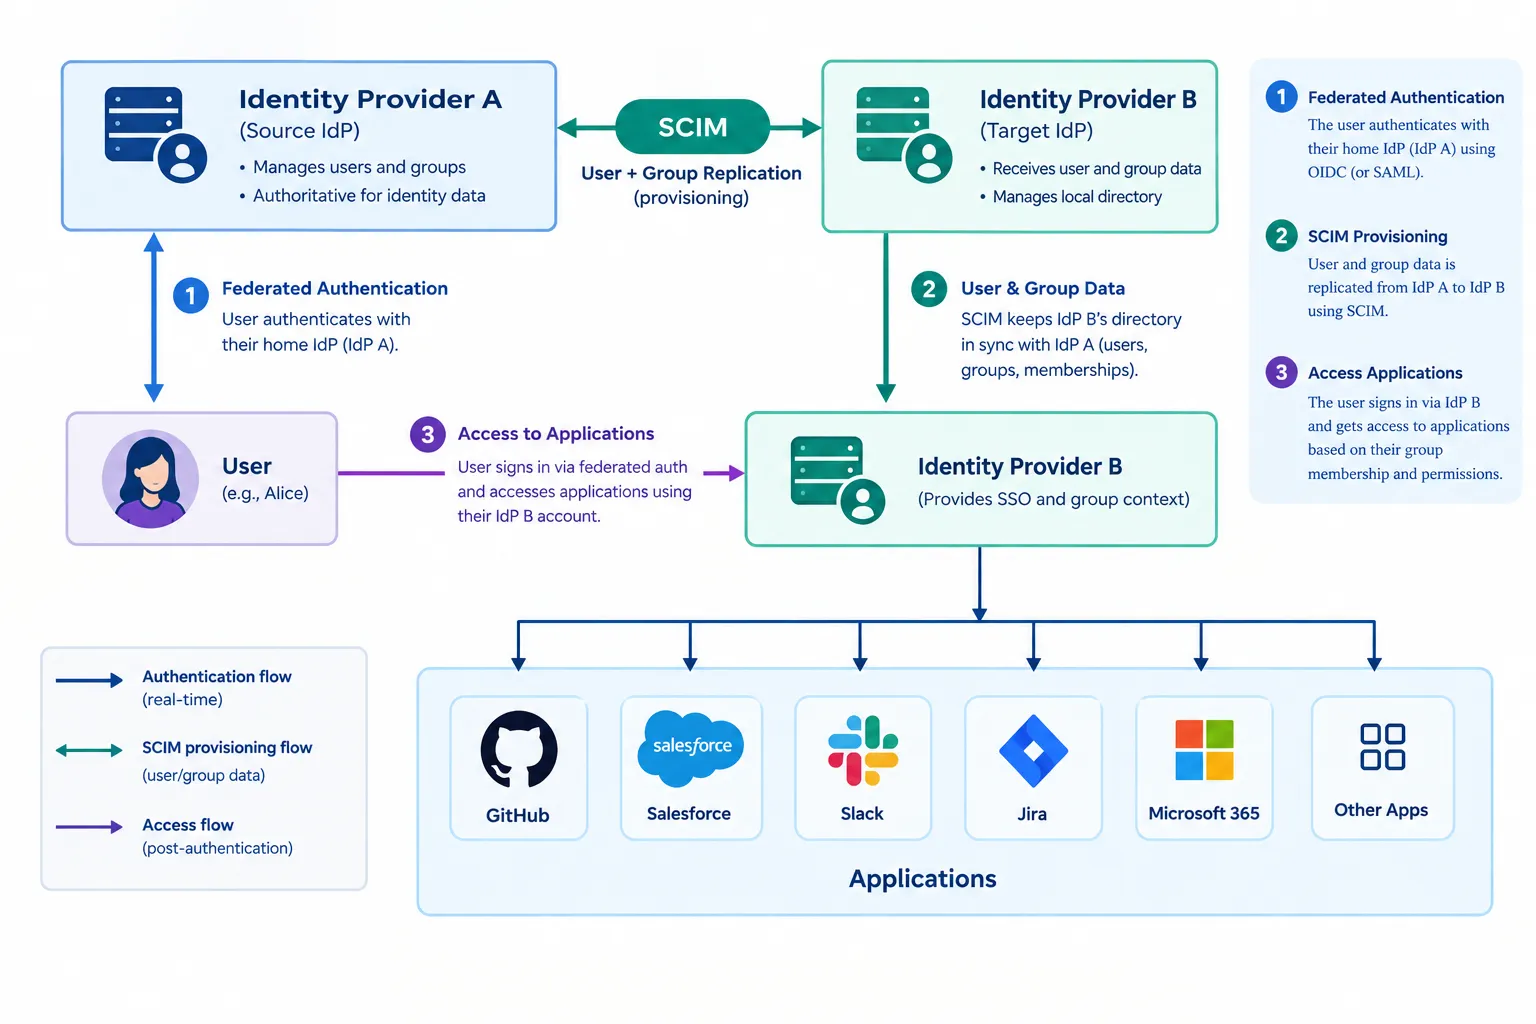
Read article: SCIM: System for Cross-Domain Identity ManagementThe Model Context Protocol, or MCP, has quickly become one of the most important pieces of infrastructure in the emerging Agentic AI ecosystem.
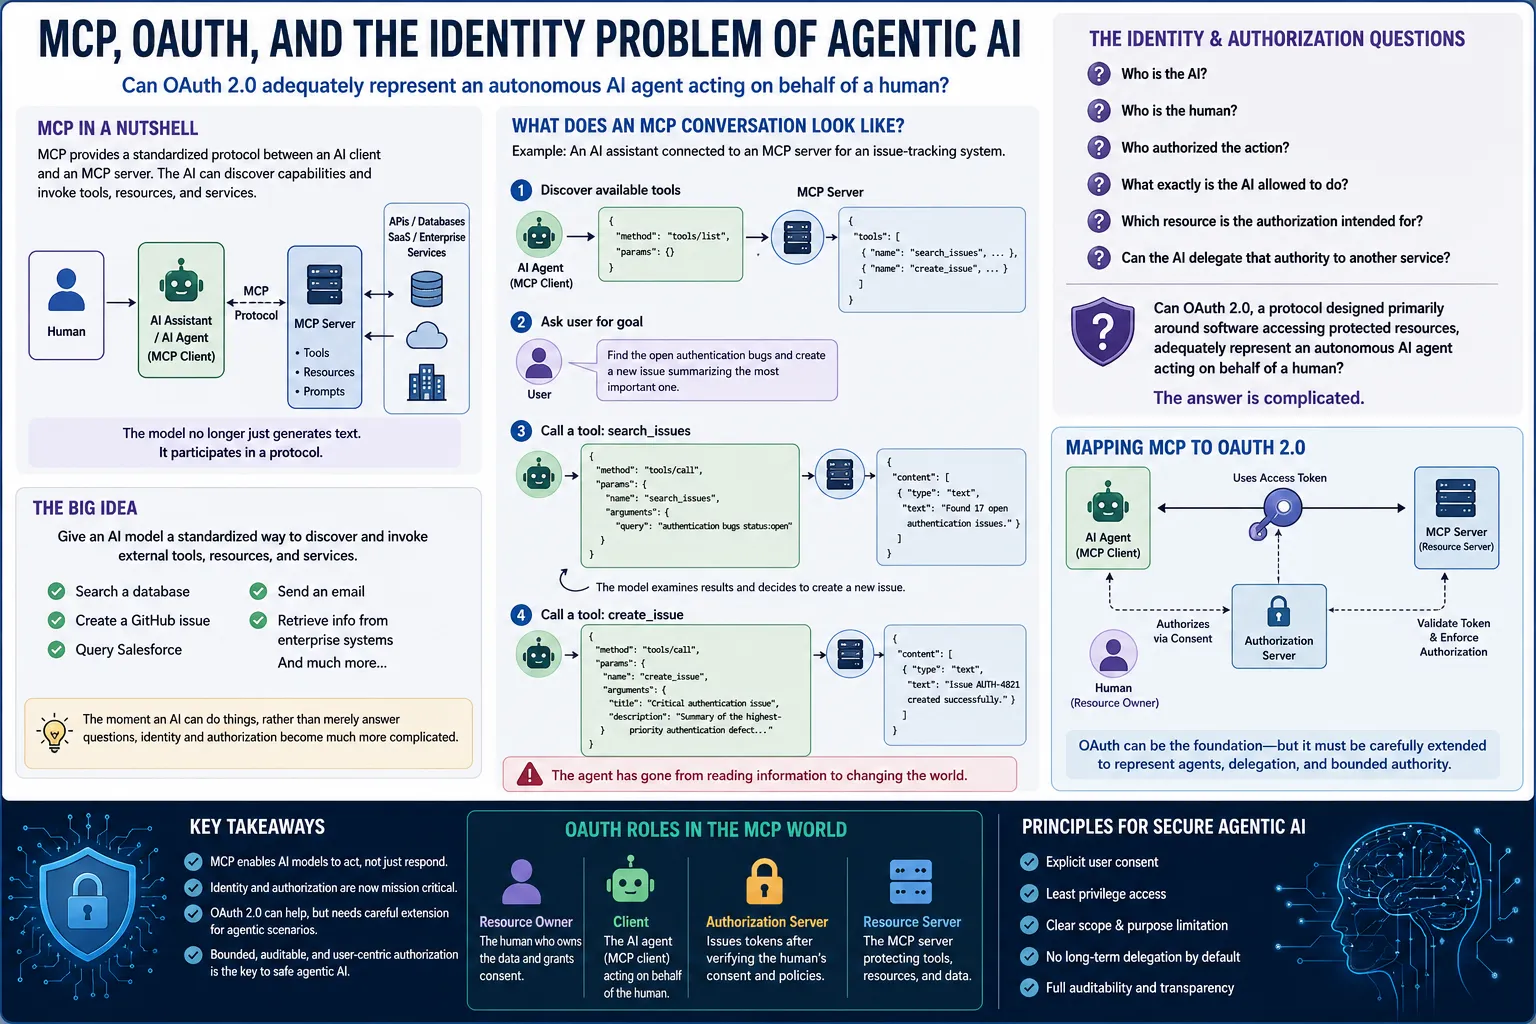
Read article: Model Context Protocol: MCP, OAuth2, and the Identity Problem of Agentic AIDelegation is a concept that has always fascinated me in the identity space. It enables secure identity propagation with tokens (assertions, tickets, etc) being properly scoped. As functionality in my Identity Protocol Debugger has continued to evolve, I wanted to add a feature that would make it…
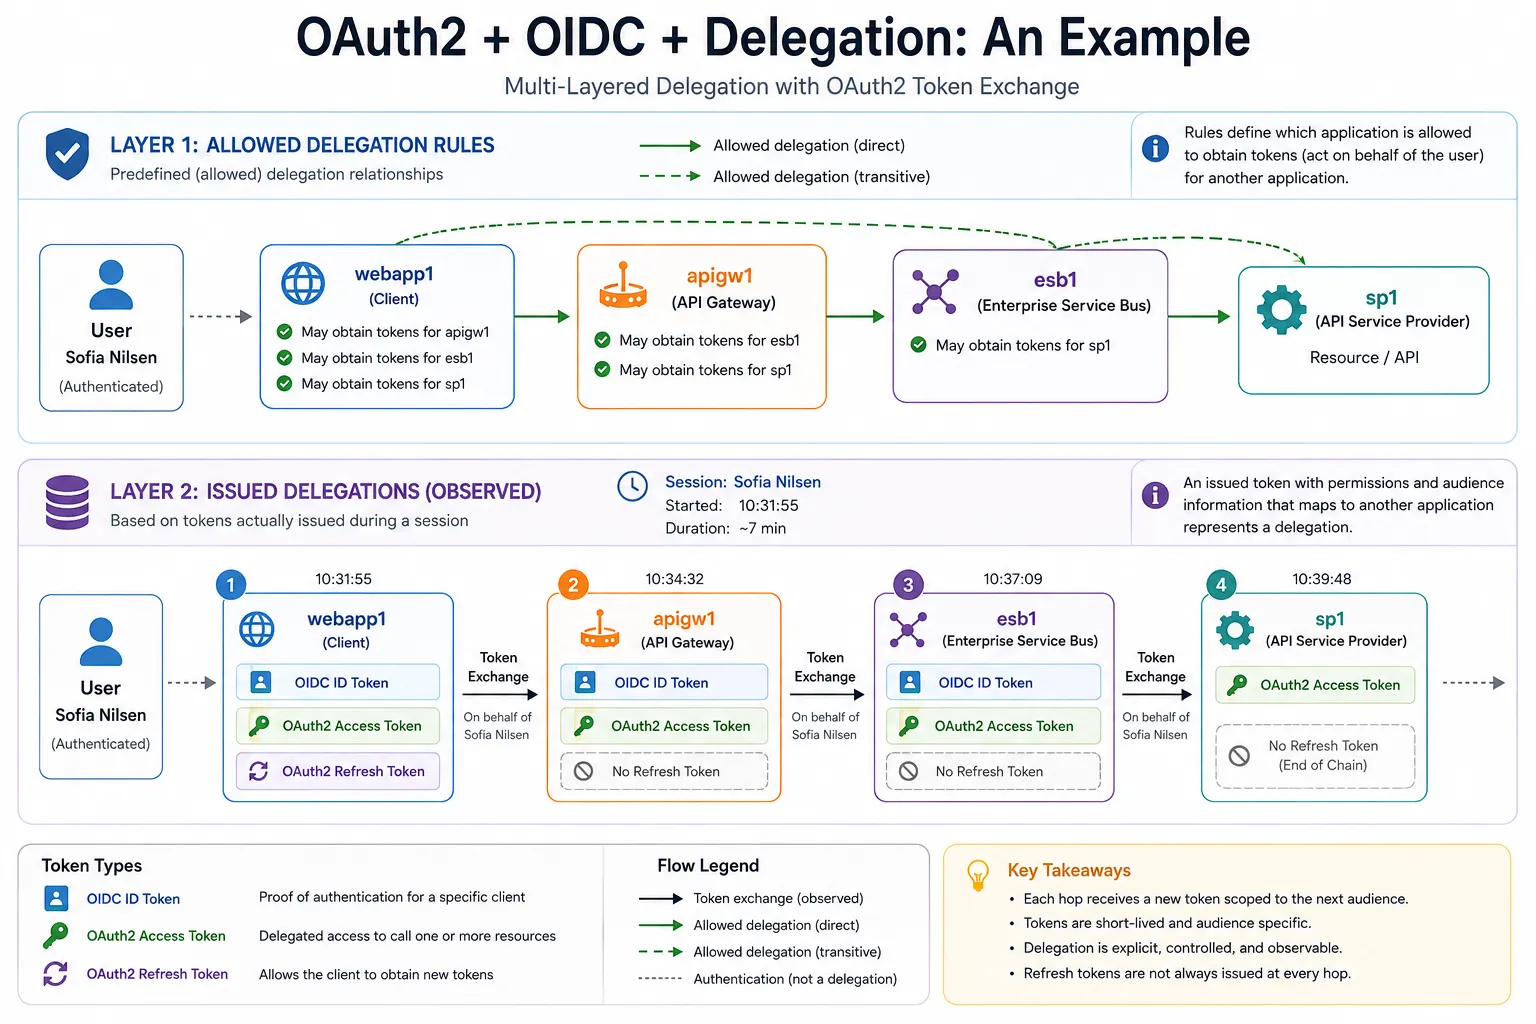
Read article: OAuth2 + OIDC + Delegation: An exampleOne of the most fundamental questions in any identity or authorization system is how does the system know that the party presenting a credential is actually entitled to use it?
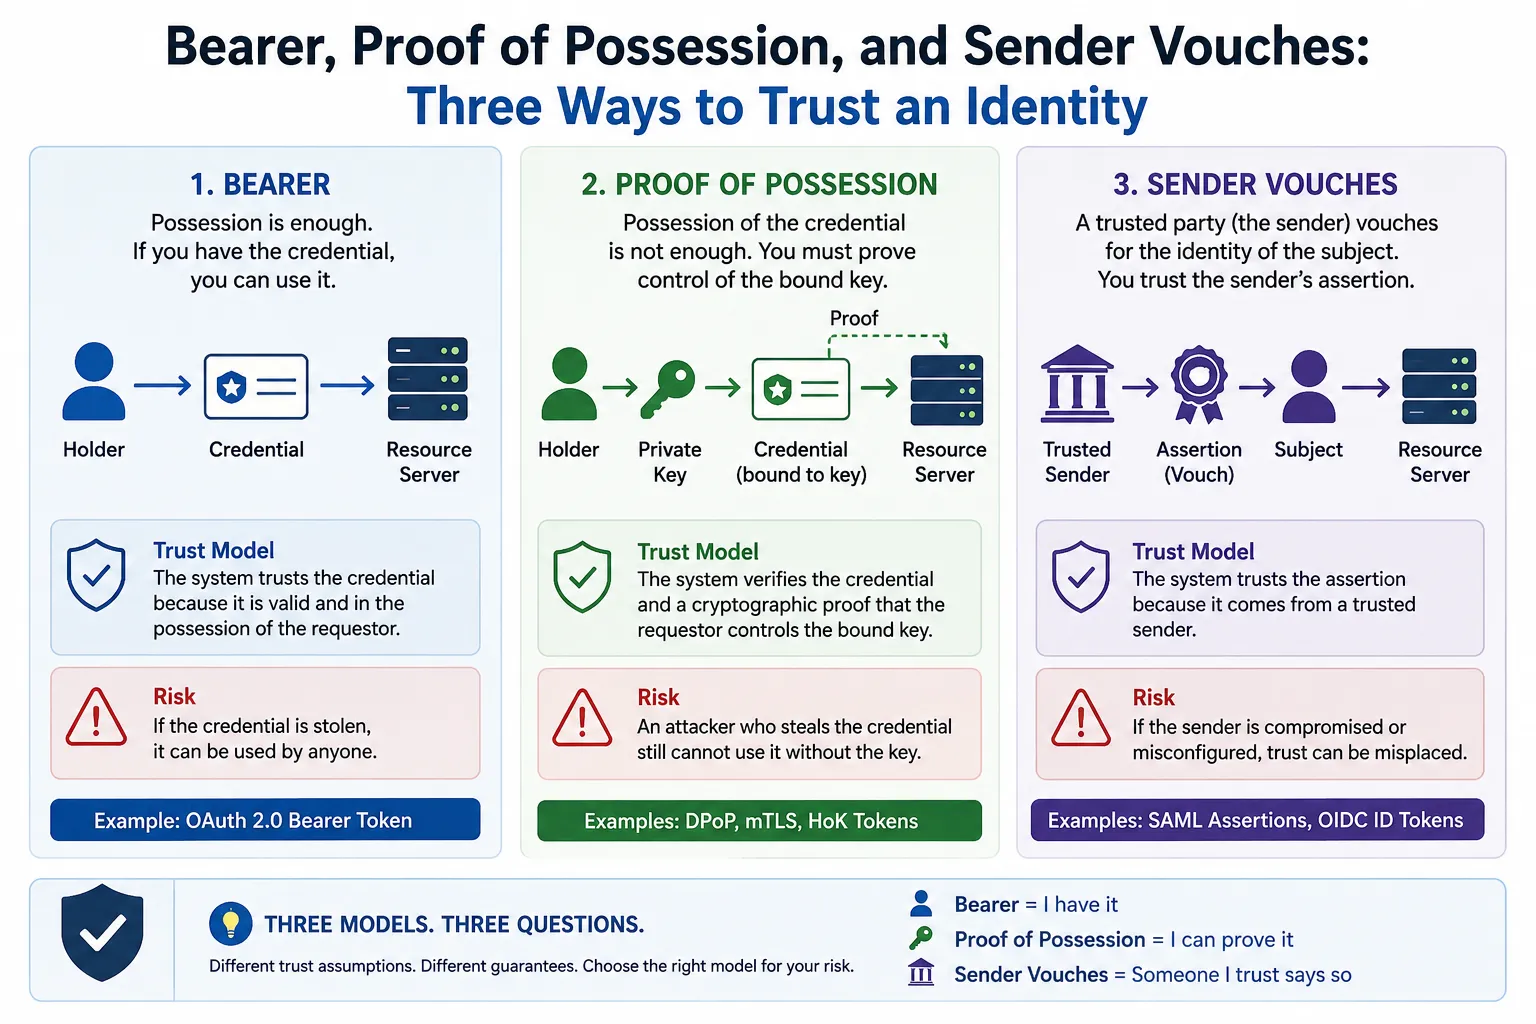
Read article: Bearer, Proof of Possession, and Sender Vouches: Three Ways to Trust an IdentityFor years, identity protocols have used phrases such as Holder of Key, Proof of Possession, Key Binding, and Bearer almost interchangeably.
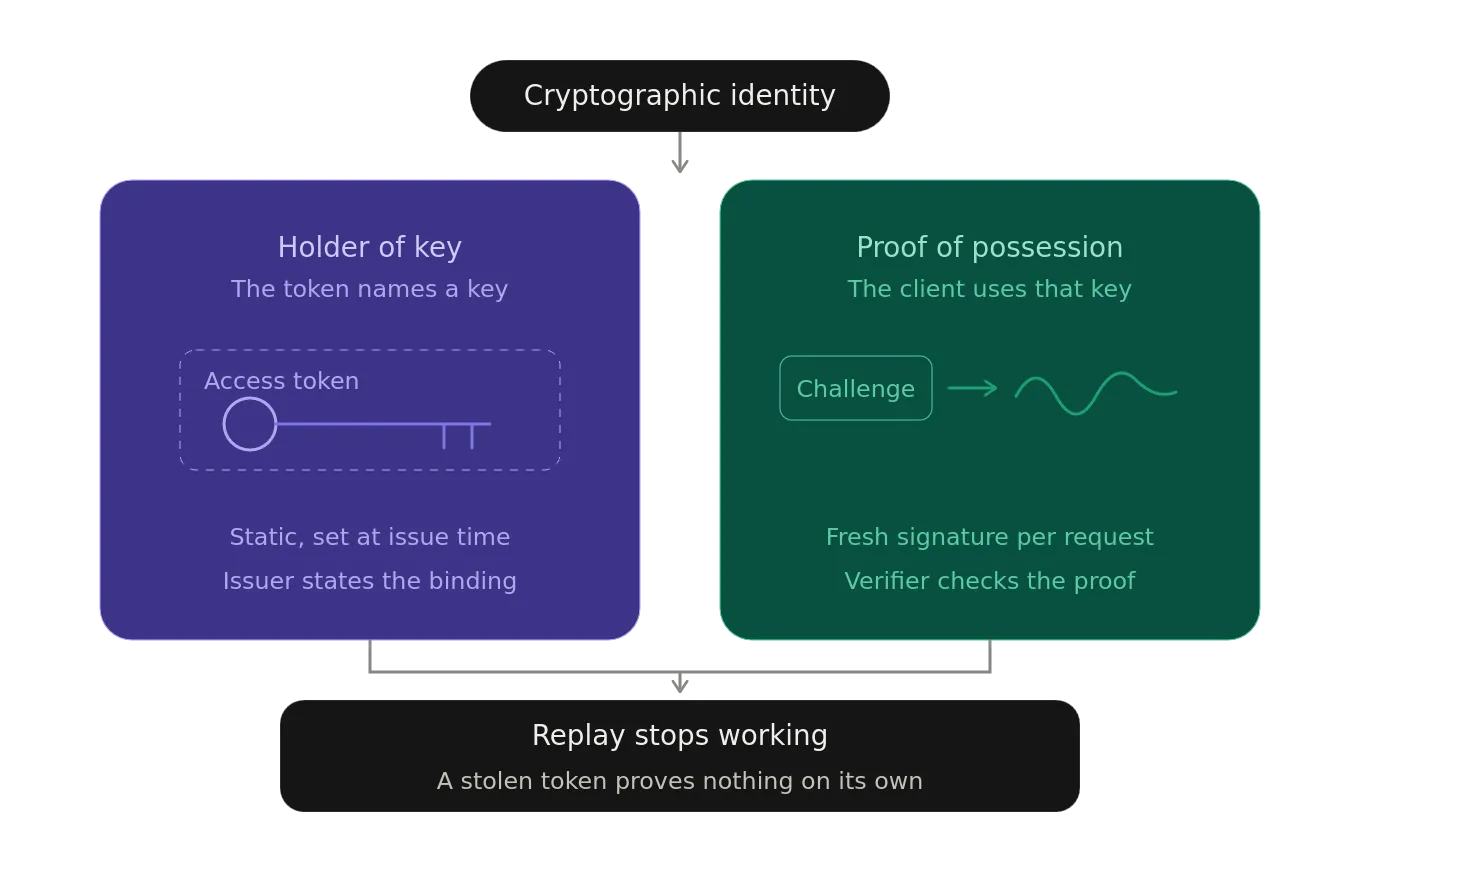
Read article: Holder of Key vs. Proof of Possession: Two Sides of Cryptographic Identity