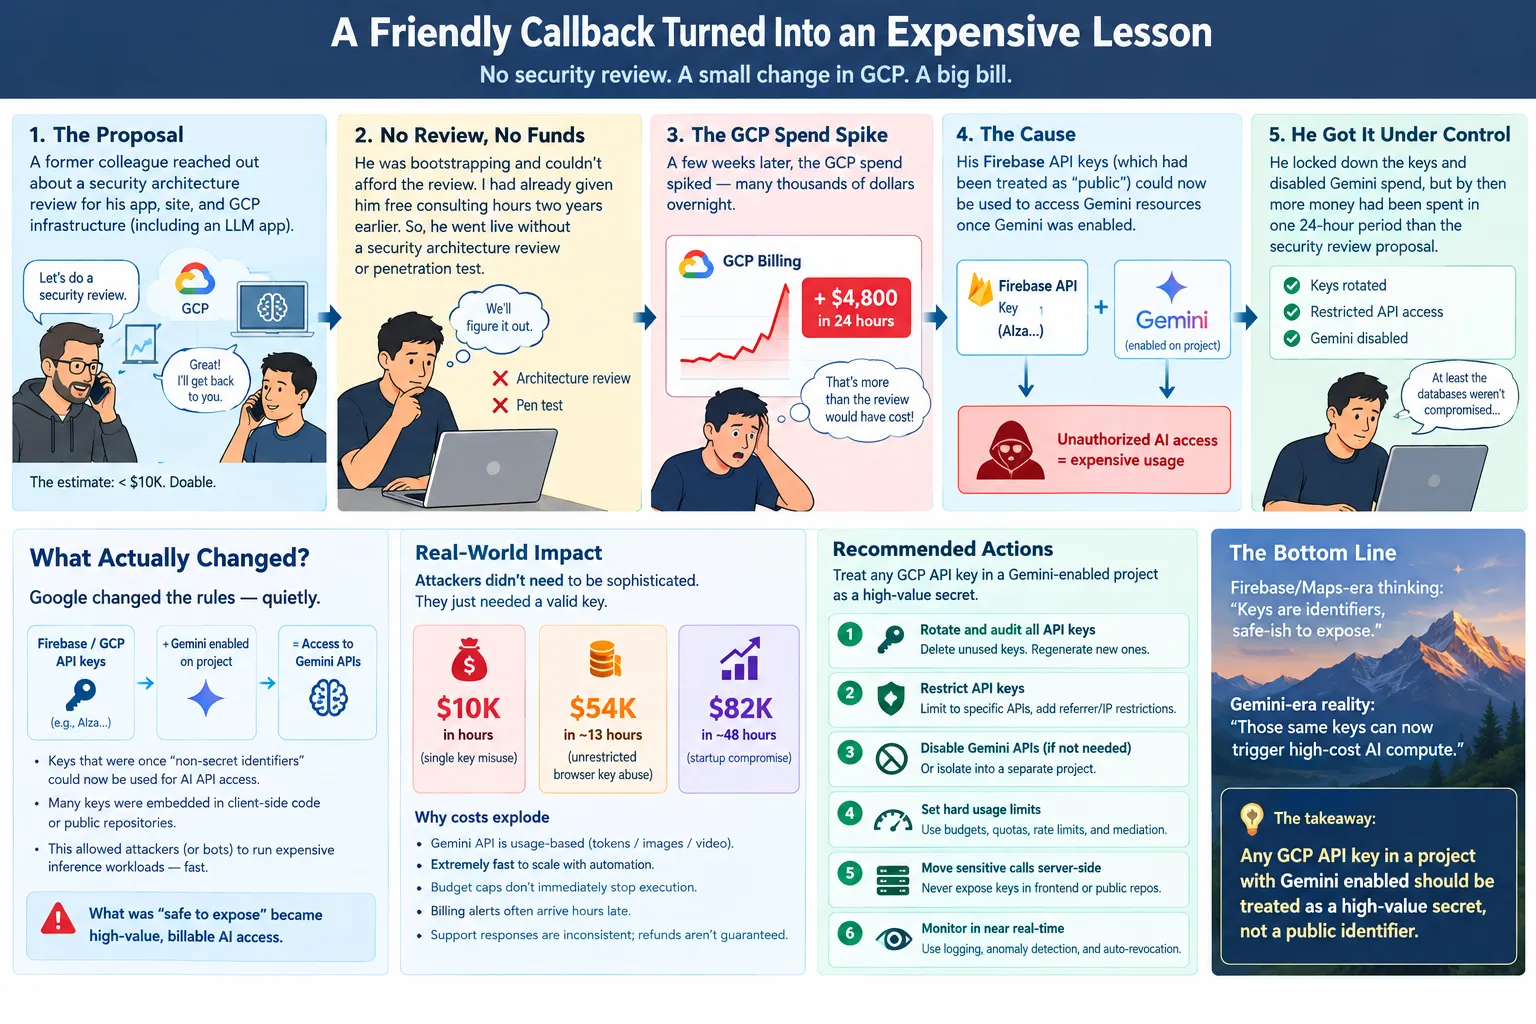
Firebase API Keys: Got a Callback From A Potential Client
I originally wrote this post about six months ago. Variations of this story have been published many times this year.
Read article: Firebase API Keys: Got a Callback From A Potential Client16 articles tagged Access Tokens.
I originally wrote this post about six months ago. Variations of this story have been published many times this year.
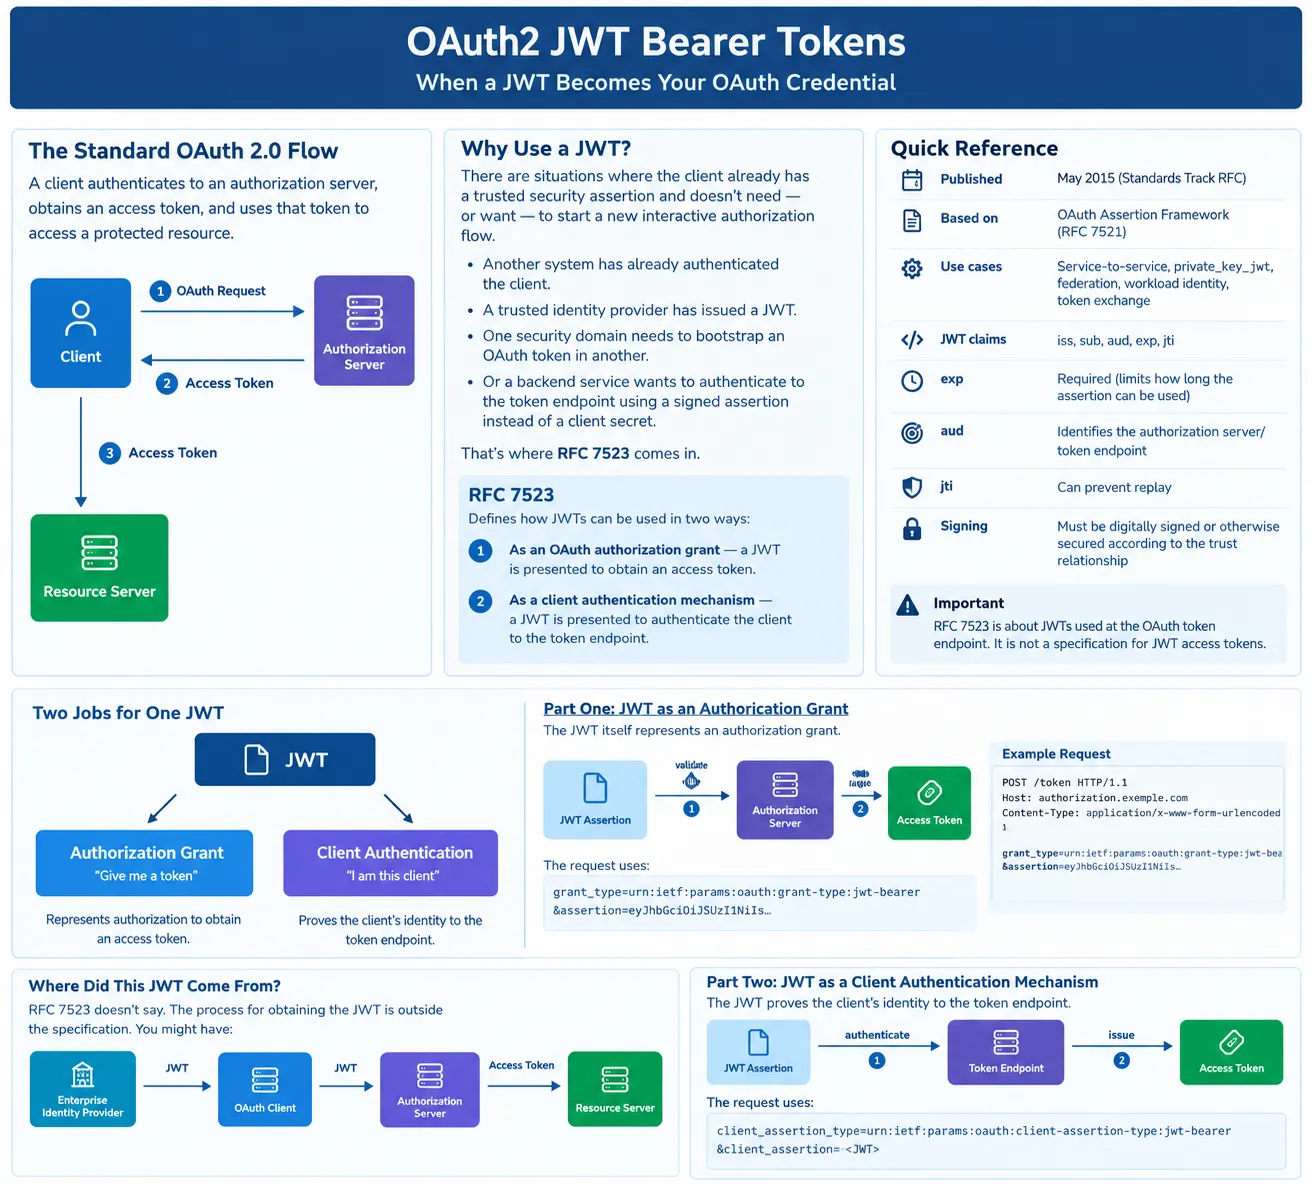
Read article: Firebase API Keys: Got a Callback From A Potential ClientOAuth2 has a fairly straightforward model. A client authenticates to an authorization server, obtains an access token, and uses that token to access a protected resource.
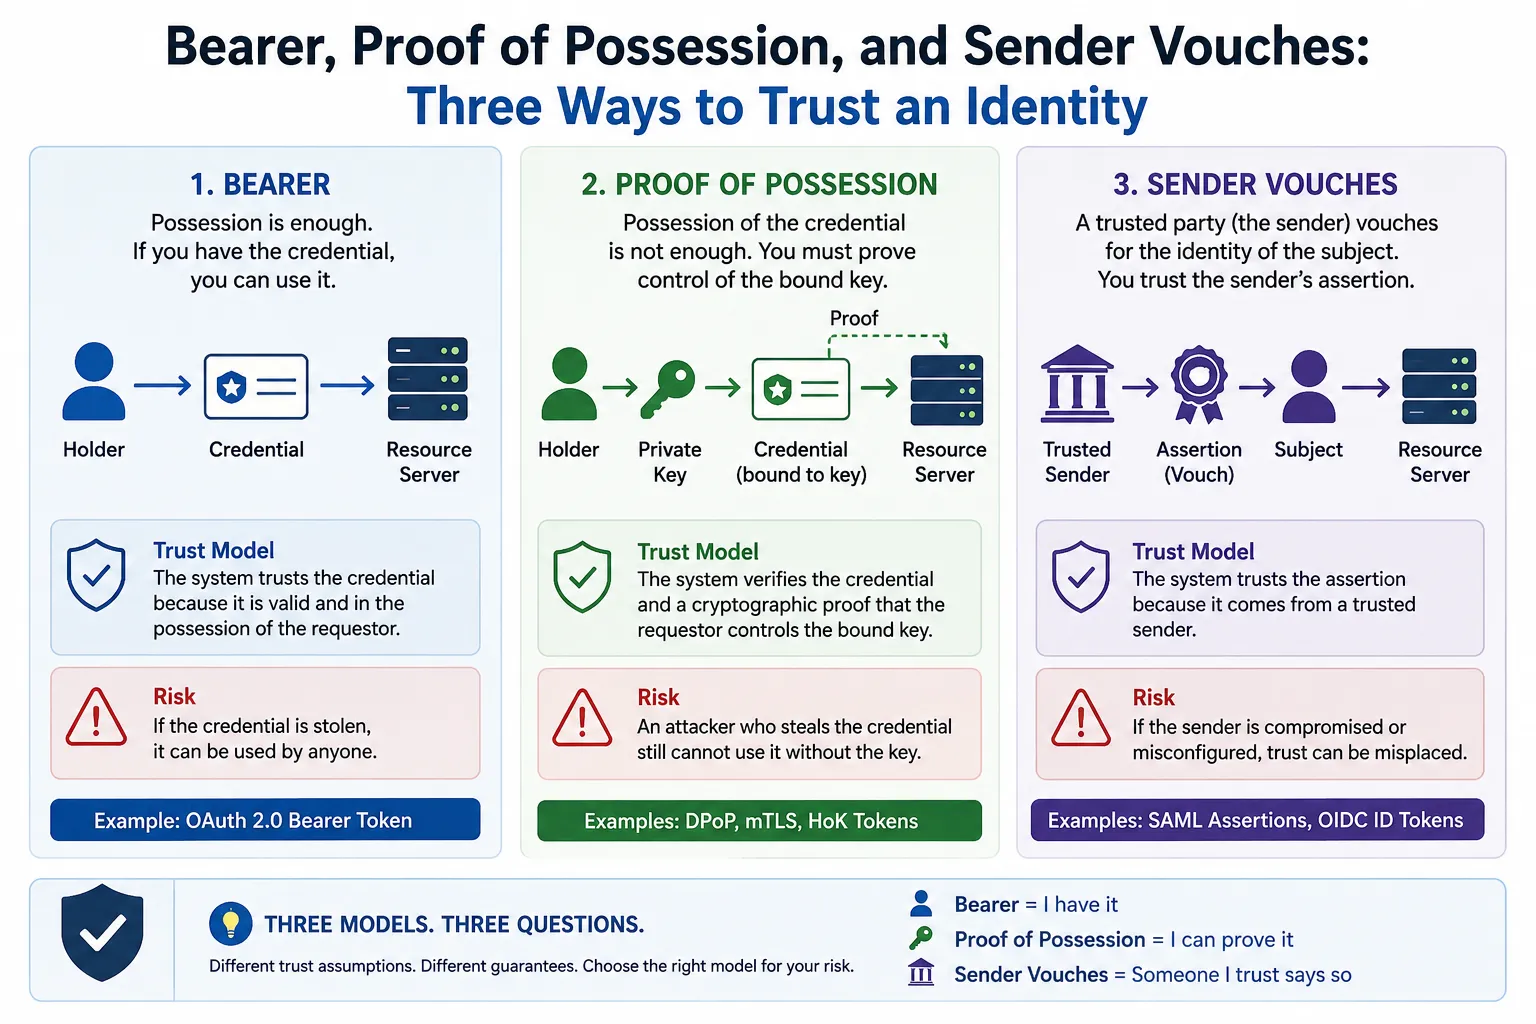
Read article: OAuth2 JWT Bearer Tokens (RFC-7523): When a JWT Becomes Your OAuth2 CredentialOne of the most fundamental questions in any identity or authorization system is how does the system know that the party presenting a credential is actually entitled to use it?
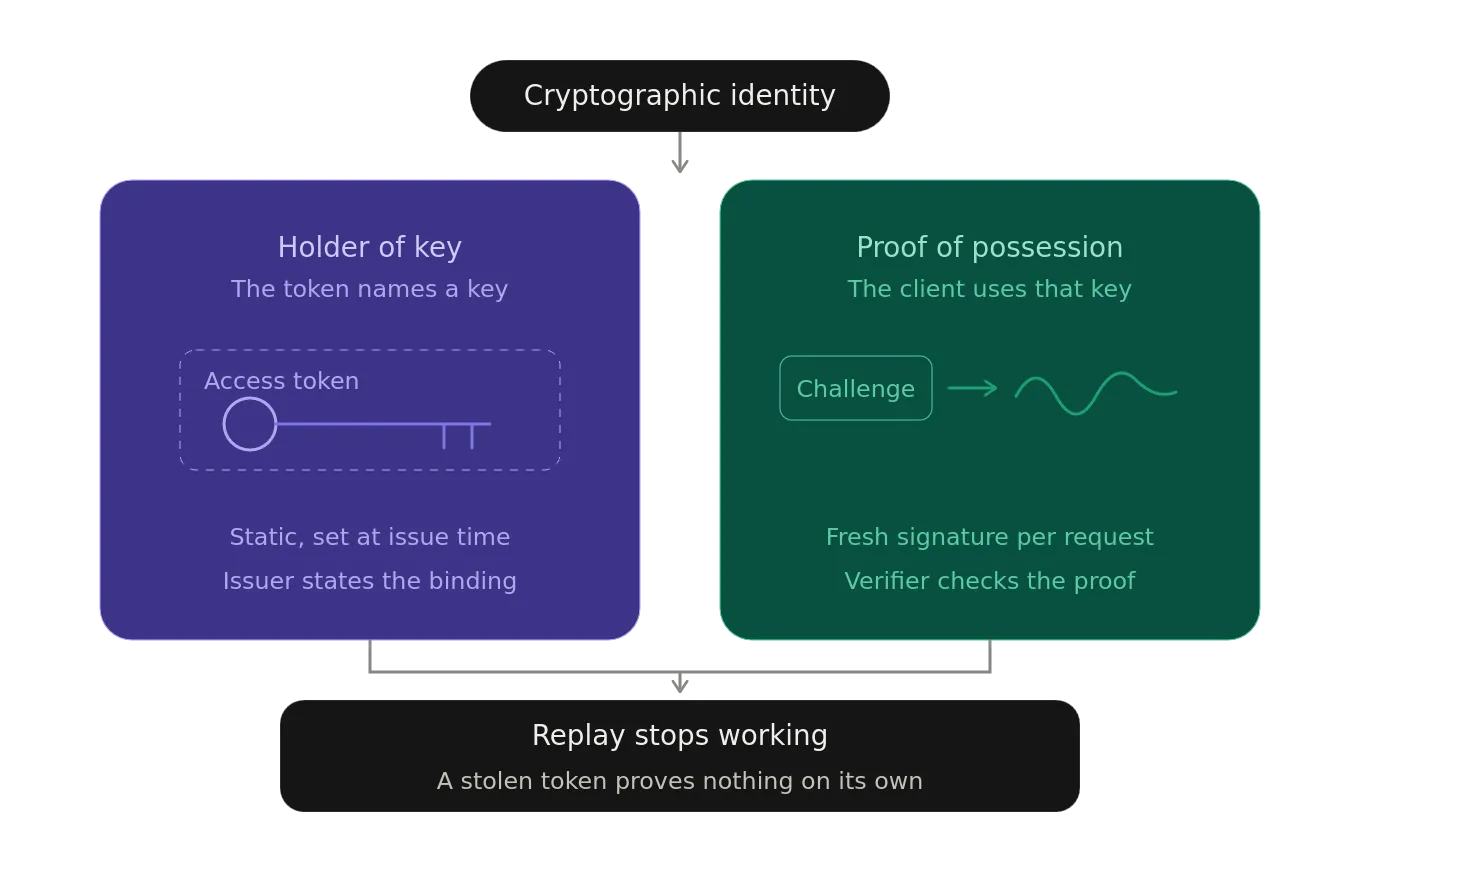
Read article: Bearer, Proof of Possession, and Sender Vouches: Three Ways to Trust an IdentityFor years, identity protocols have used phrases such as Holder of Key, Proof of Possession, Key Binding, and Bearer almost interchangeably.
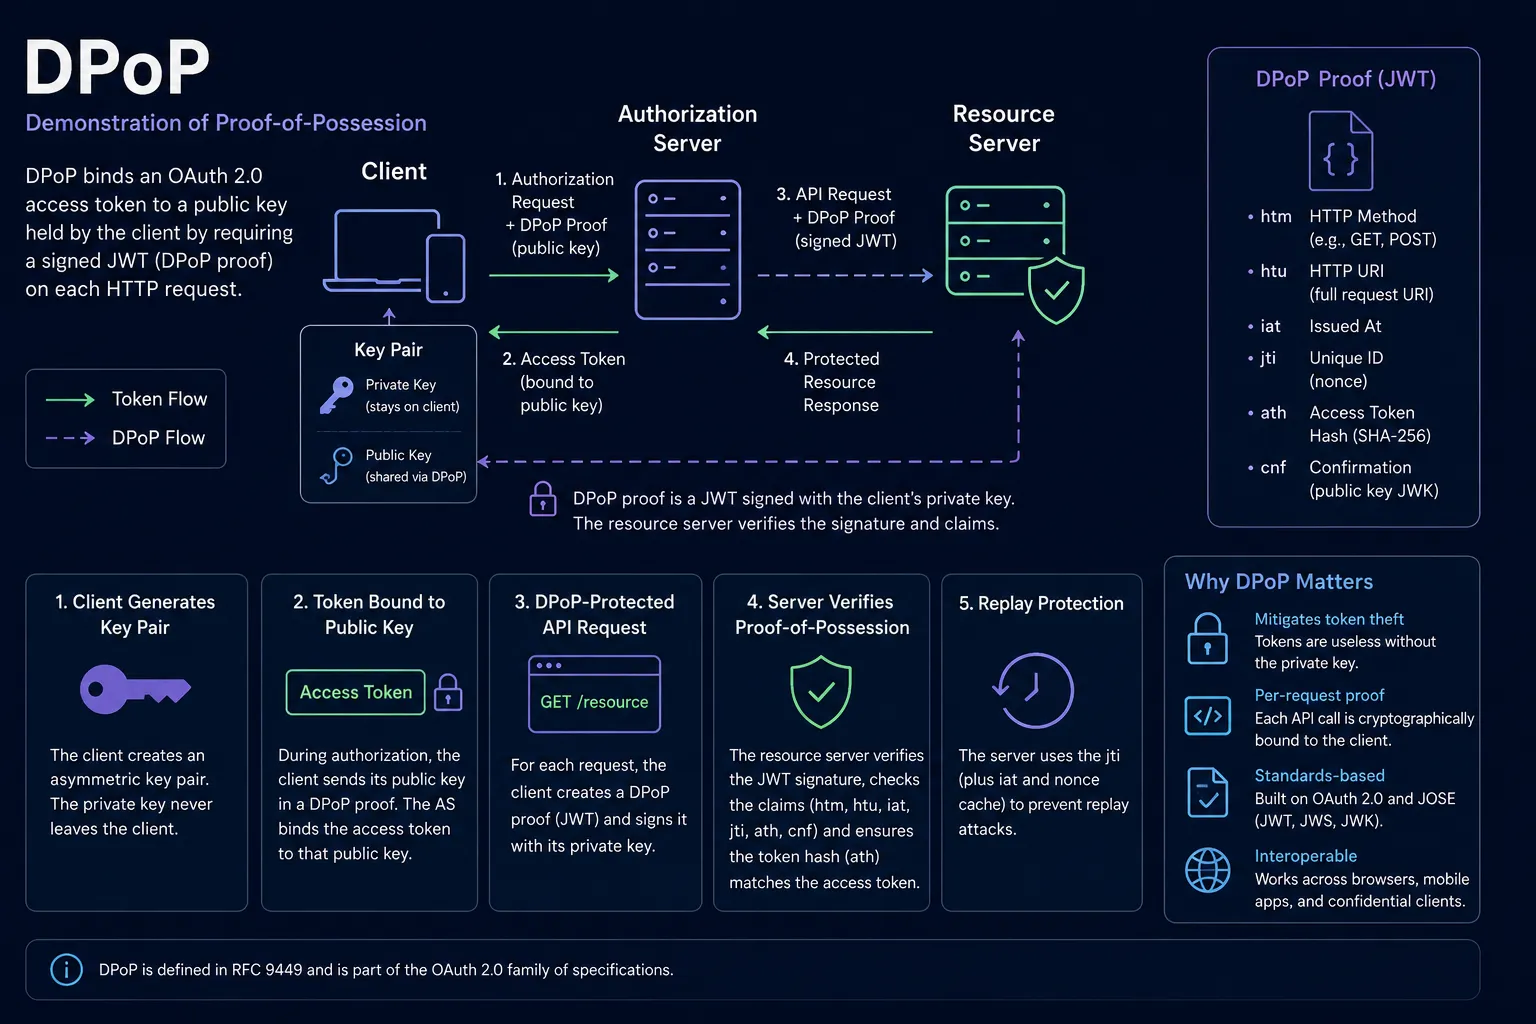
Read article: Holder of Key vs. Proof of Possession: Two Sides of Cryptographic IdentityOAuth2 has long suffered from a fundamental weakness: bearer tokens.
Read article: DPoP: The Missing Security Layer in OAuth2 and OID4VCIOAuth2 has always had a fundamental problem: a bearer token is a bearer token. After all, it’s a bearer token.
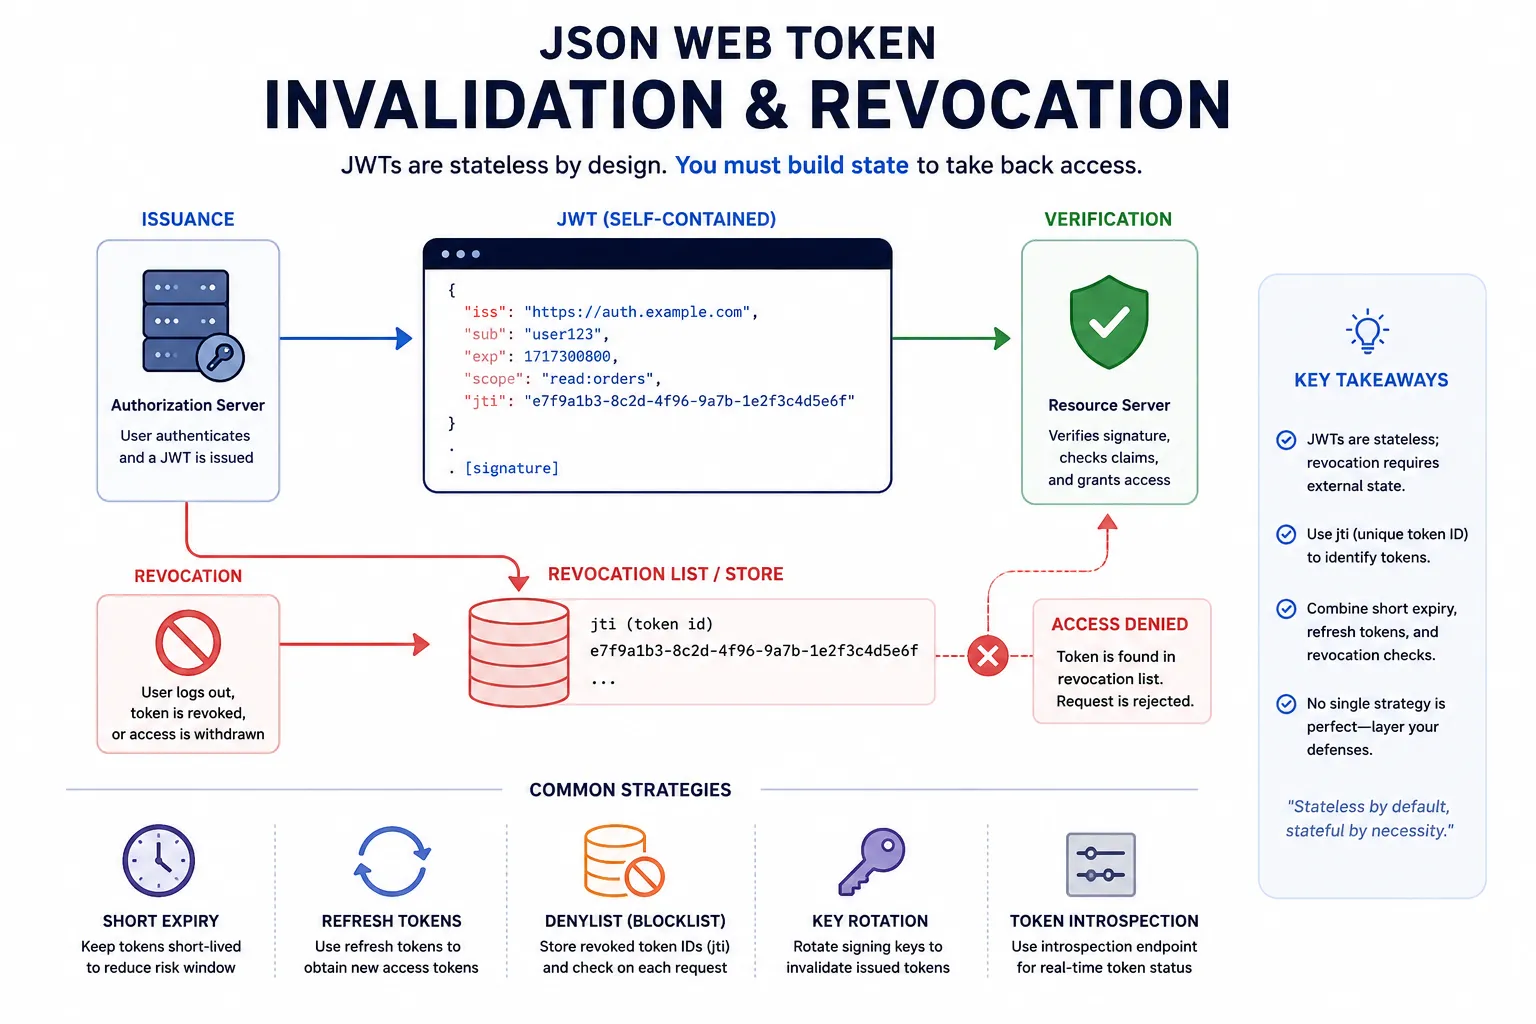
Read article: DPoP Support Comes to the Identity Protocol DebuggerI’ve touched on the topic of using JWT as an Access Token on several previous blog posts:
Read article: JWT as Oauth2 Access Tokens & Refresh Tokens— Invalidation: The Awkward RealityFor anyone who has been paying attention, this blog post has been a long-time coming for multiple reasons. First, this is my first blog post in a couple of years — I’ve been heads down on a couple of projects for awhile now. This is literally the first time I’ve “come up for air” since the last…
Read article: RFC 9068: A JWT-Based OAuth2 Access Token Format StandardThere are several approaches to securing APIs. Every API Gateway vendor supports the same core set of API security mechanisms. API Keys and OAuth2 are two examples of these authentication (plus authorization) mechanism. When should one be used over the other? What are the differences between the…
Read article: OAuth2 Access Tokens vs API Keys — Using JWTsThis article is a place my other blog posts can point at when referencing this series.
Read article: OAuth2 Access Tokens and Multiple Resources Series