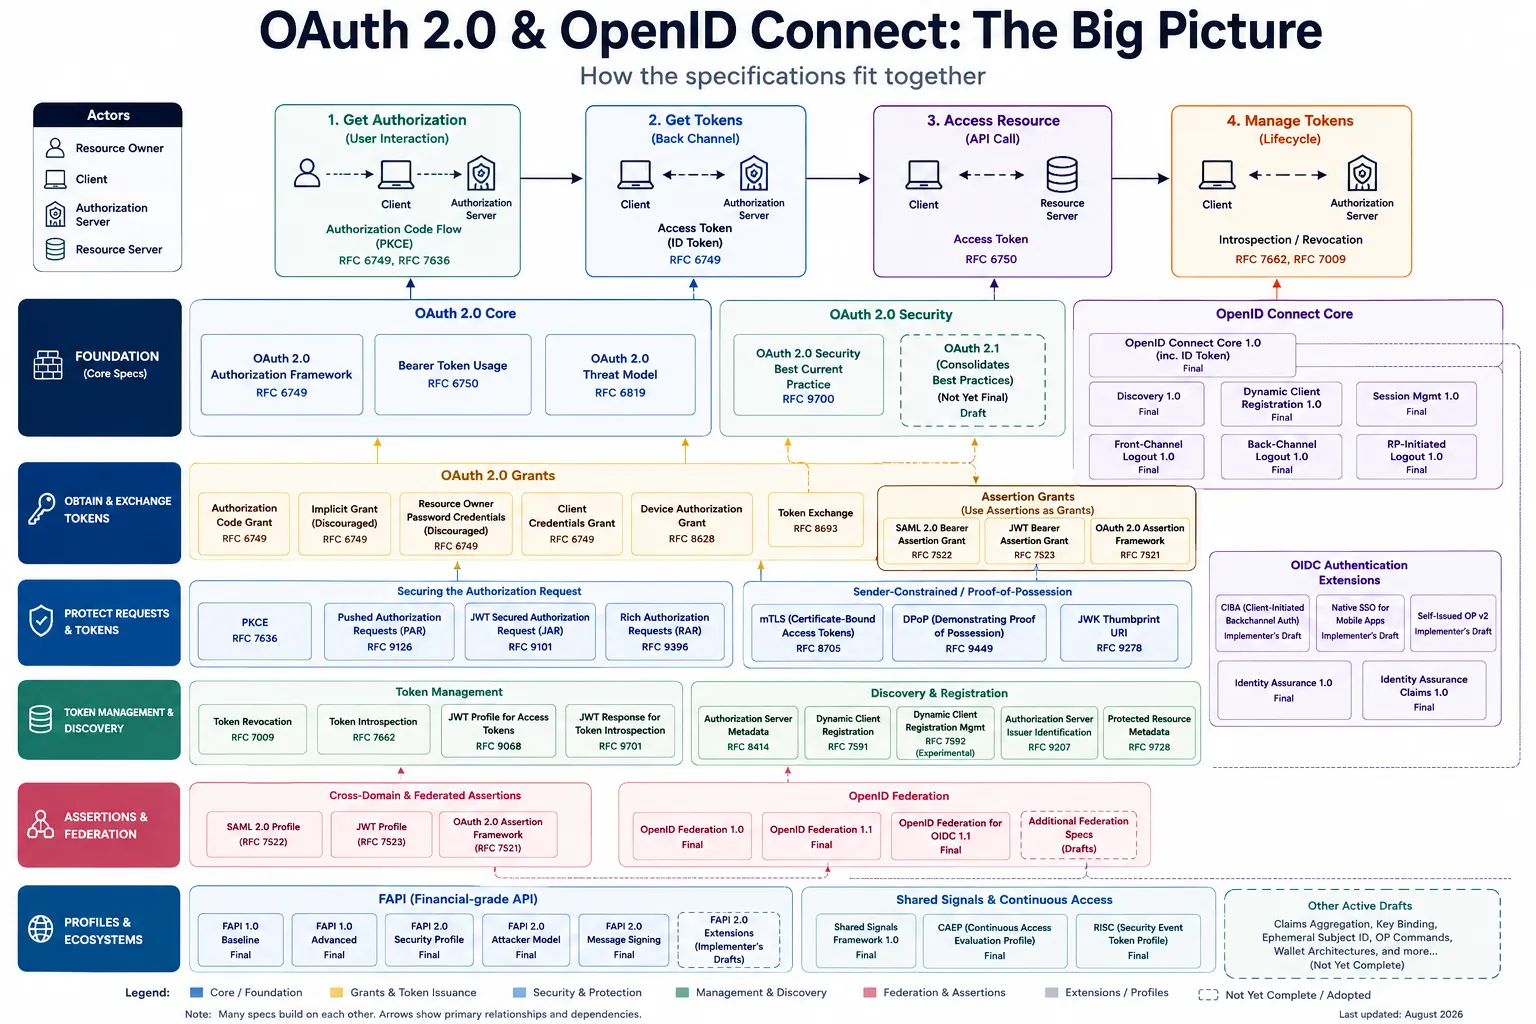
OAuth2 + OIDC: All of the Specs (2026 Edition)
Current as of August, 2026.
Read article: OAuth2 + OIDC: All of the Specs (2026 Edition)Notes on application security, API security, identity, and API management from the field. Articles are also published on Medium. Browse the archive by topic instead — 124 subjects.
Current as of August, 2026.
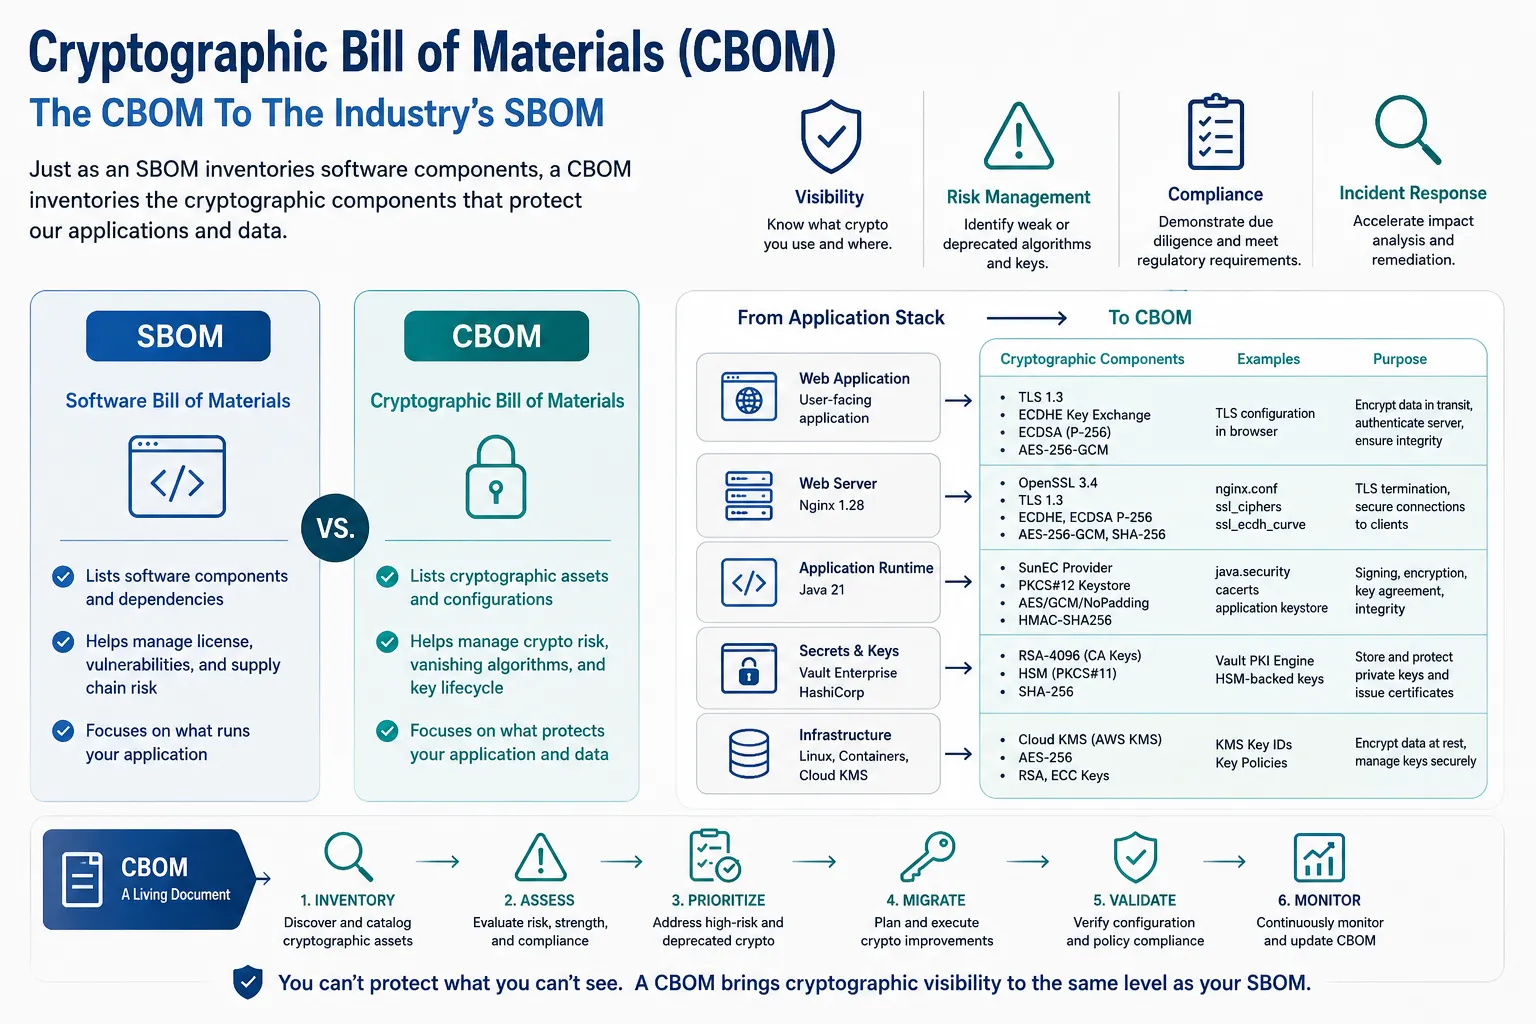
Read article: OAuth2 + OIDC: All of the Specs (2026 Edition)A Cryptographic Bill of Materials (CBOM) is exactly what it sounds like: an inventory of every cryptographic component used throughout an organization. If a Software Bill of Materials (SBOM) tells you what software you have, a CBOM tells you how that software is protected.
Read article: Cryptographic Bill of Materials: The CBOM To The Industry’s SBOMDisclaimer: I’m not a lawyer. I’m just trying to understand how this works.
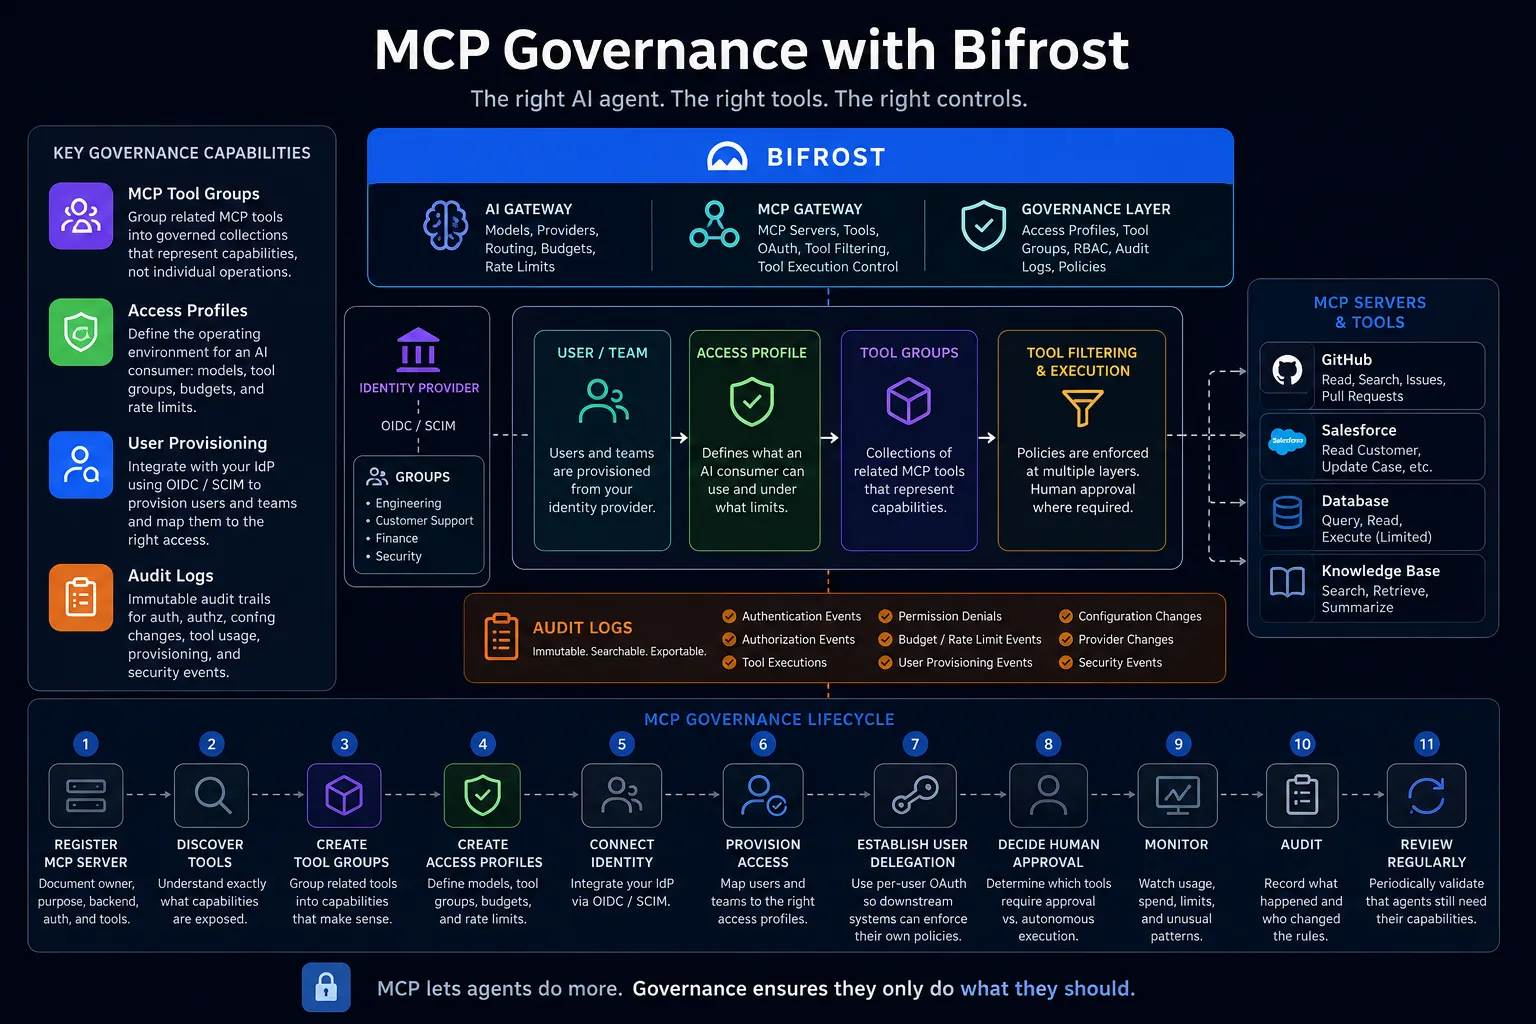
Read article: Digital Death: Legal FrameworksThe Model Context Protocol (MCP) has changed the relationship between an LLM and the systems around it.
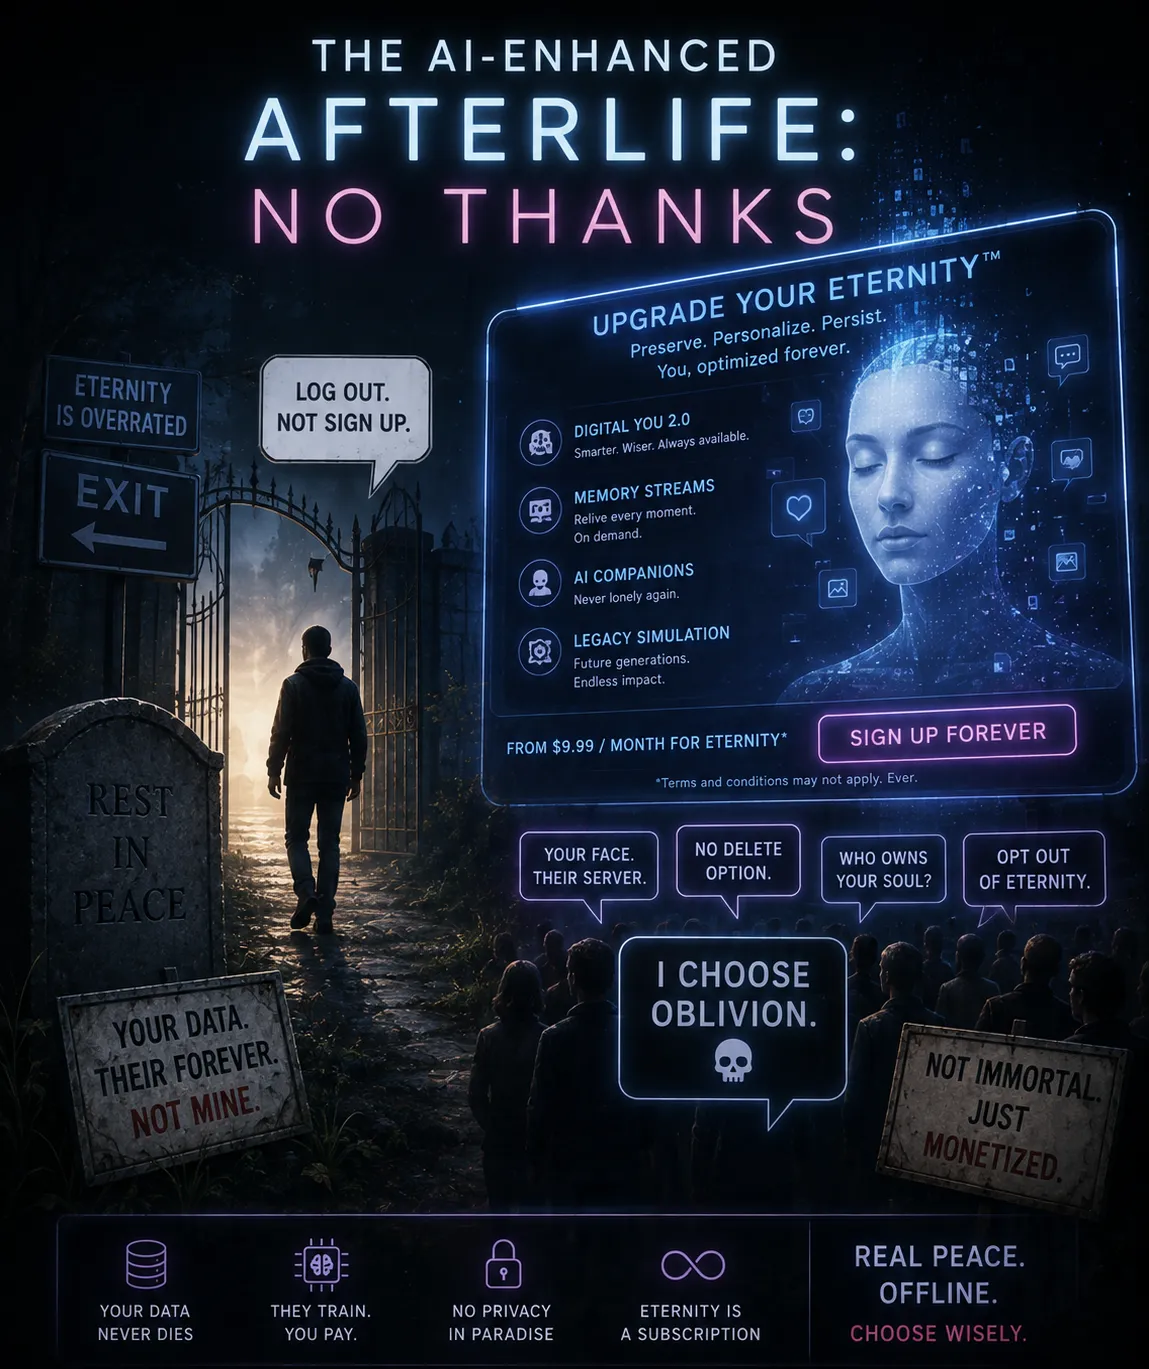
Read article: MCP Governance With Bifrost AI GatewayI like this one. It sits right at the intersection of AI, identity, law, and just enough existential dread to make people double-check their password manager.
Read article: The AI-Enhanced Afterlife: No ThanksI started thinking about this post a while back when I saw a former colleague’s Medium profile still listed as following mine. He died in the early days of covid. A quick check showed that his LinkedIn profile seems to have disappeared — not sure how that works. It was still there a few years ago.
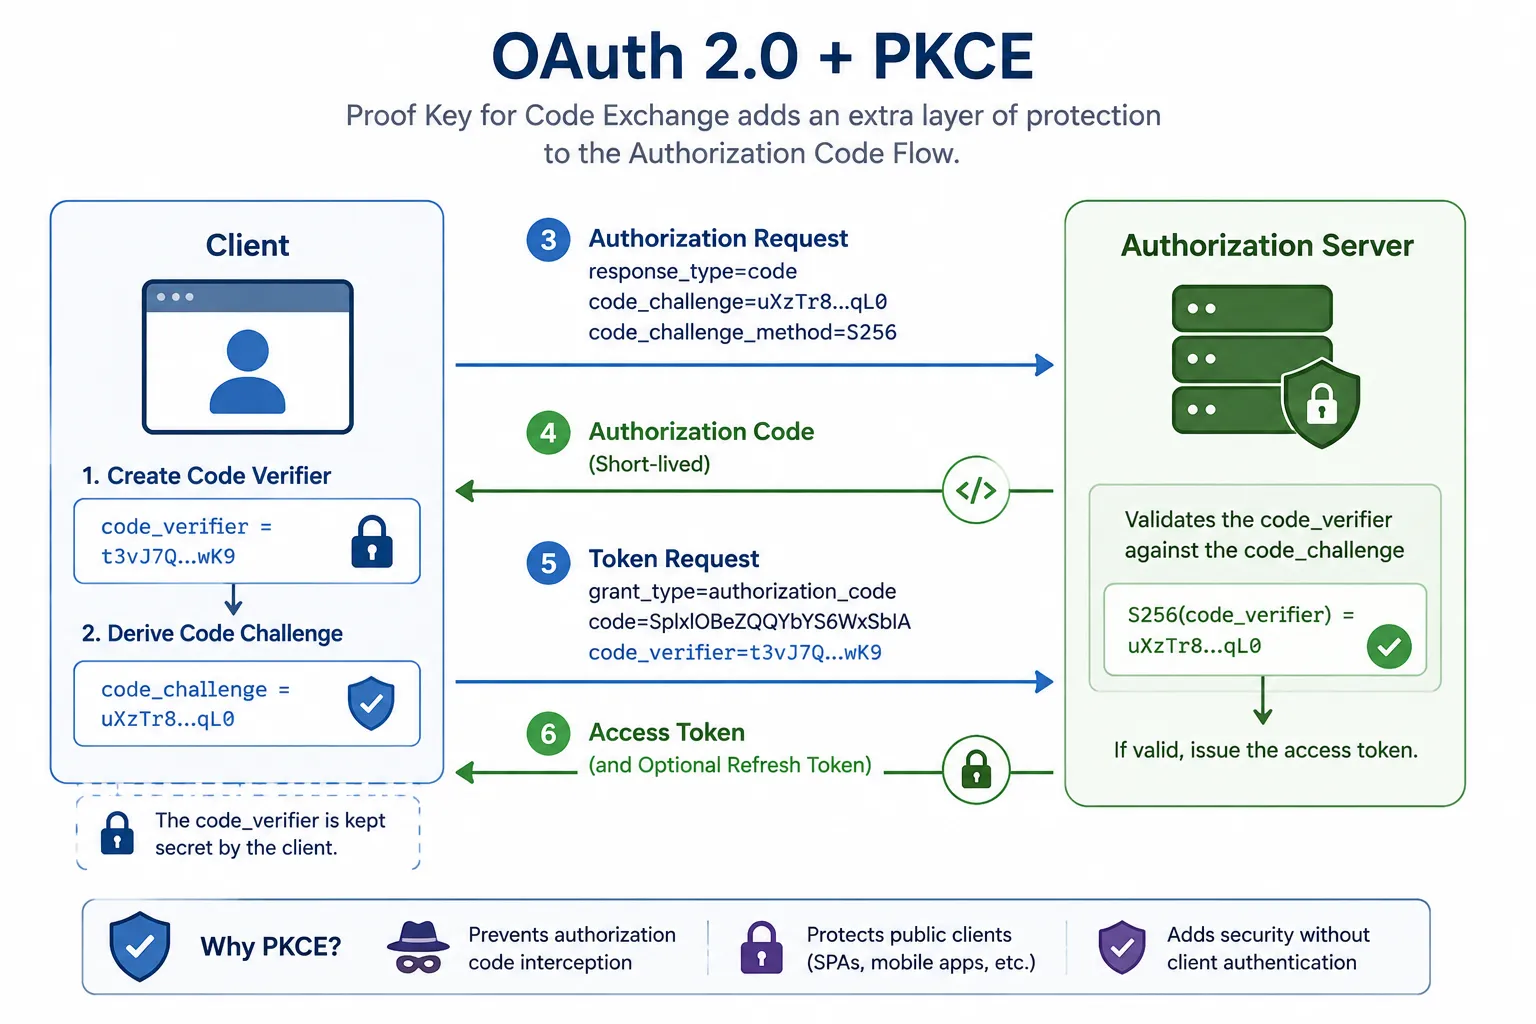
Read article: The Digital Dead: Existence Beyond Death OnlineOne of the biggest misconceptions about OAuth2 is that it is a single protocol. In reality, OAuth2 has evolved considerably over the years as new attack vectors have been discovered and new security mechanisms introduced. One of the most significant of these improvements is Proof Key for Code…
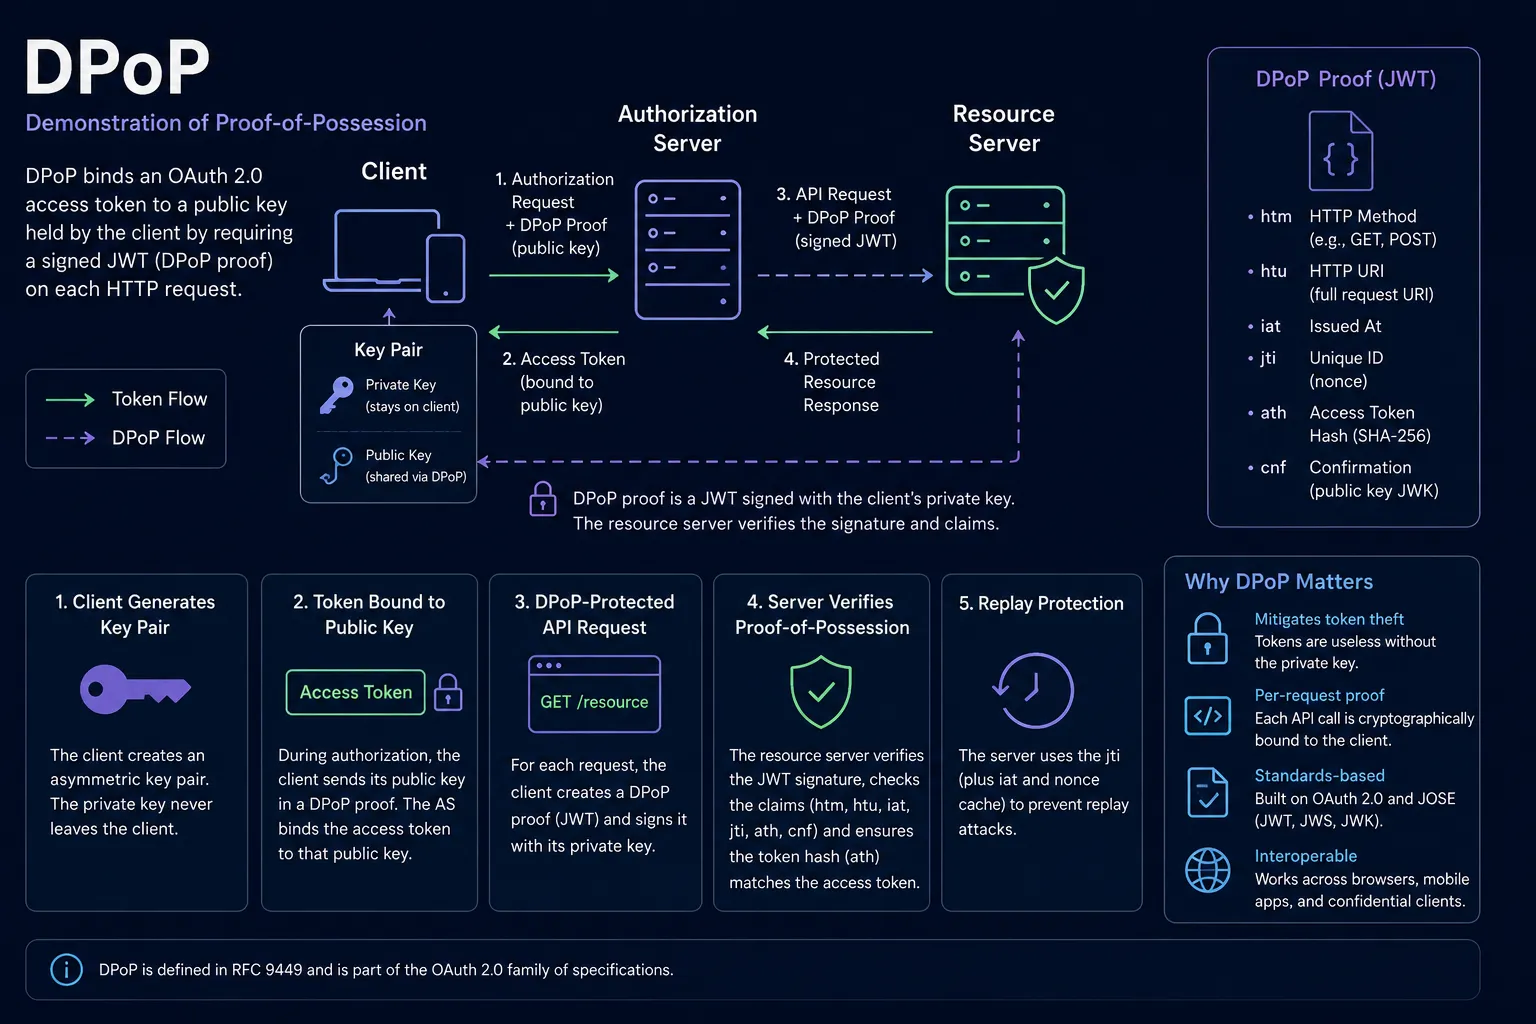
Read article: PKCE: Proof Key for Code ExchangeOAuth2 has long suffered from a fundamental weakness: bearer tokens.
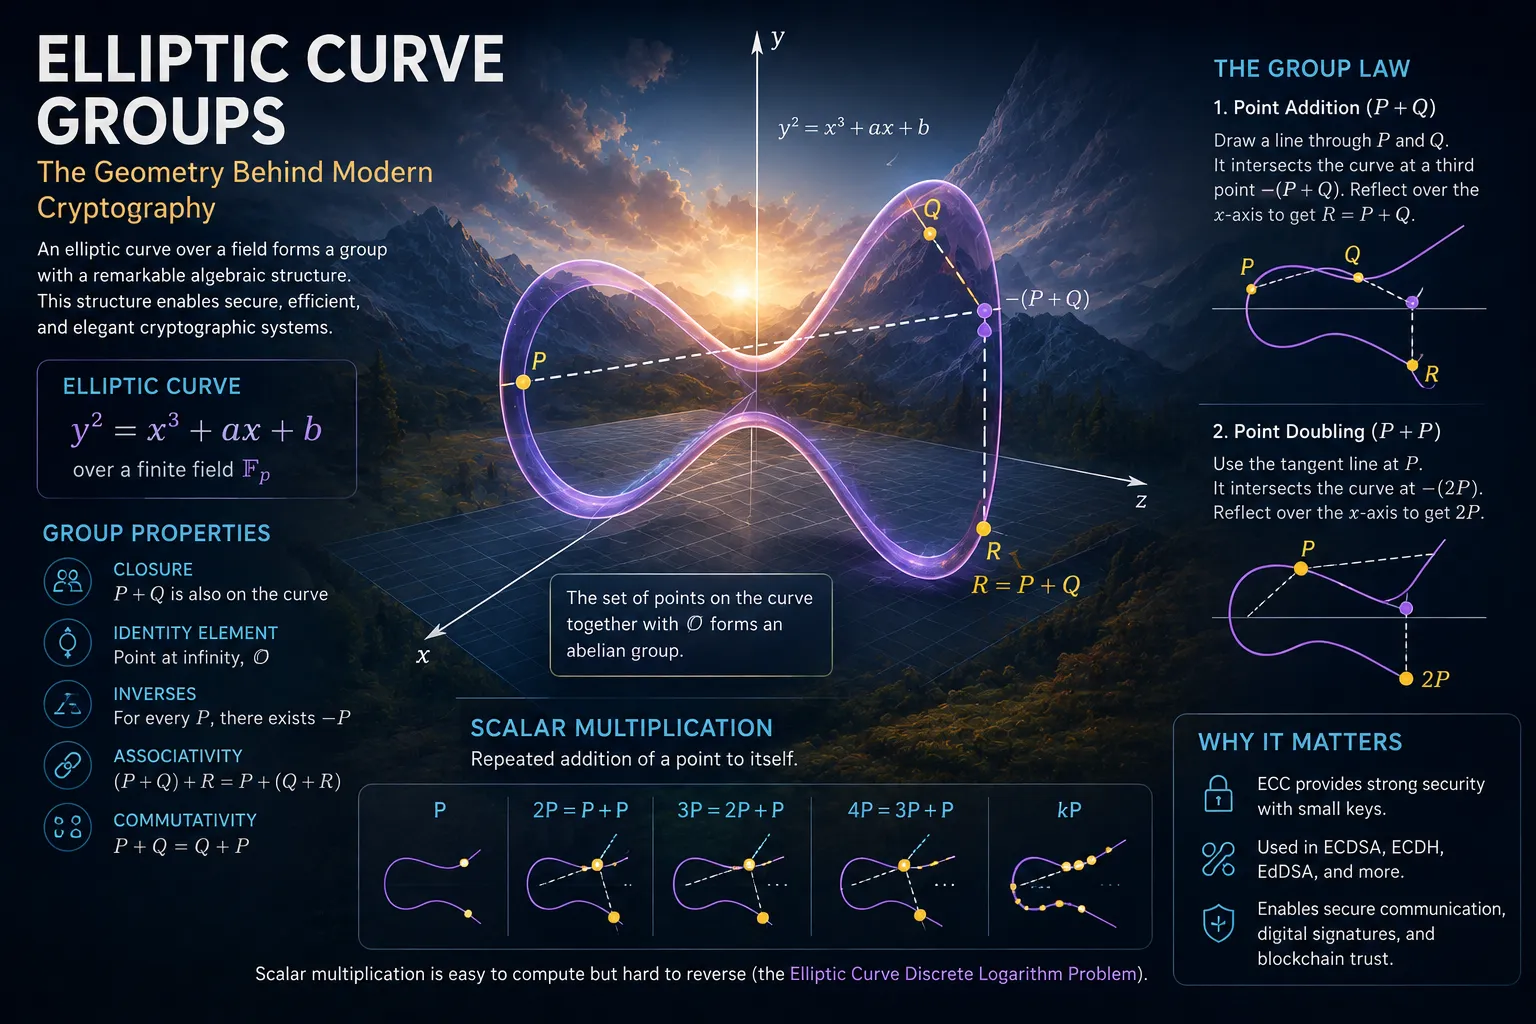
Read article: DPoP: The Missing Security Layer in OAuth2 and OID4VCIIf you’ve ever read a specification like WebAuthn, DID Core, SD-JWT VC, BBS Signatures, OID4VCI, or OID4VP, you’ve probably encountered references to P-256, secp256k1, Ed25519, or BLS12–381.
Read article: Elliptic Curve Groups: The Mathematical Engine Behind Modern Digital IdentityWhen we think about algorithms, we often imagine a computer executing a series of instructions:
Read article: Discrete Algorithms: The Mathematics of Decisions, Networks, and Digital IntelligenceLooking for something specific? Browse all 124 topics.