Announcements

Iya-STS Achieves OpenID Connect Conformance Certification

Iya-STS v1.0.0 has completed the OpenID Foundation’s OpenID Connect self-certification process. On November 5, 2026, the Foundation published certifications for eleven conformance profiles across OpenID Connect authentication and logout.

The seven OpenID Provider profiles are Basic, Implicit, Hybrid, Configuration, Dynamic Registration, Form Post, and Third-Party Initiated Login. The four Logout profiles are RP-Initiated Logout, Session Management, Front-Channel Logout, and Back-Channel Logout.

Iya-STS began as a small component for testing identity integrations. It has grown into an identity provider and integration platform covering OAuth 2.0, SAML, WS-Trust, Kerberos, LDAP, SCIM, PKI, WebAuthn, XACML, and more. The design goal has been to implement open standards instead of adding another set of proprietary integration mechanisms. Conformance certification is a publicly documented declaration of conformance against specific protocol profiles.

More certification profiles and continued work on the platform are planned.
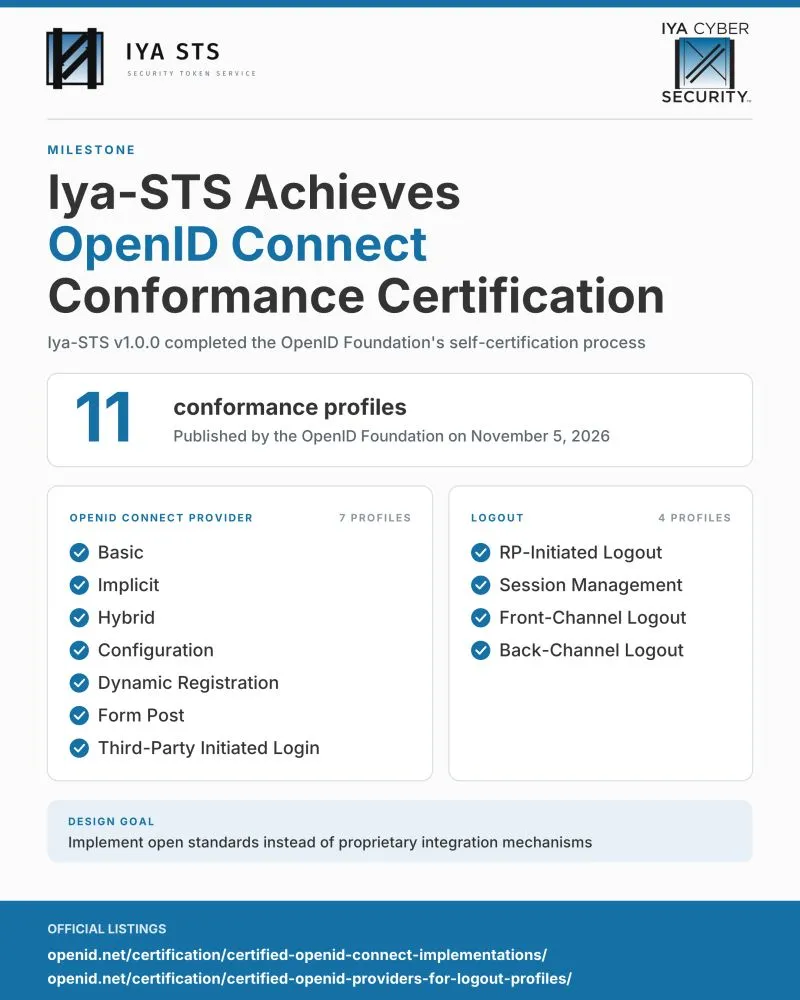
Infographic: Iya-STS Achieves OpenID Connect Conformance Certification. Iya-STS v1.0.0 completed the OpenID Foundation’s self-certification process. Eleven conformance profiles, published by the OpenID Foundation on November 5, 2026. OpenID Connect Provider, seven profiles: Basic, Implicit, Hybrid, Configuration, Dynamic Registration, Form Post, and Third-Party Initiated Login. Logout, four profiles: RP-Initiated Logout, Session Management, Front-Channel Logout, and Back-Channel Logout. Design goal: implement open standards instead of proprietary integration mechanisms.

Certified OpenID Connect implementations · Certified logout profiles
Introducing Iya-STS v1.0.0: Identity Integration for the AI Era

Iya-STS is an identity provider and integration platform. It started as a mock Security Token Service inside the Identity Protocol Debugger, built to test identity integrations, and grew into directory services, PKI, authorization engines, and federation until it had a purpose of its own.

Most organizations already run several identity products across different protocols and trust relationships. Iya-STS brings twelve areas of identity standards together, so applications don’t have to deal with each provider and token format separately.

As AI agents, MCP-based systems, and workload identities join human users, token exchange (RFC 8693) and delegation matter more, because systems need to know who is acting and on whose authority.

Version 1.0.0 also coincides with the OpenID Foundation publishing our OpenID Connect certifications: eleven conformance profiles across OpenID Provider and Logout. That program is self-certification, and the test data is public.

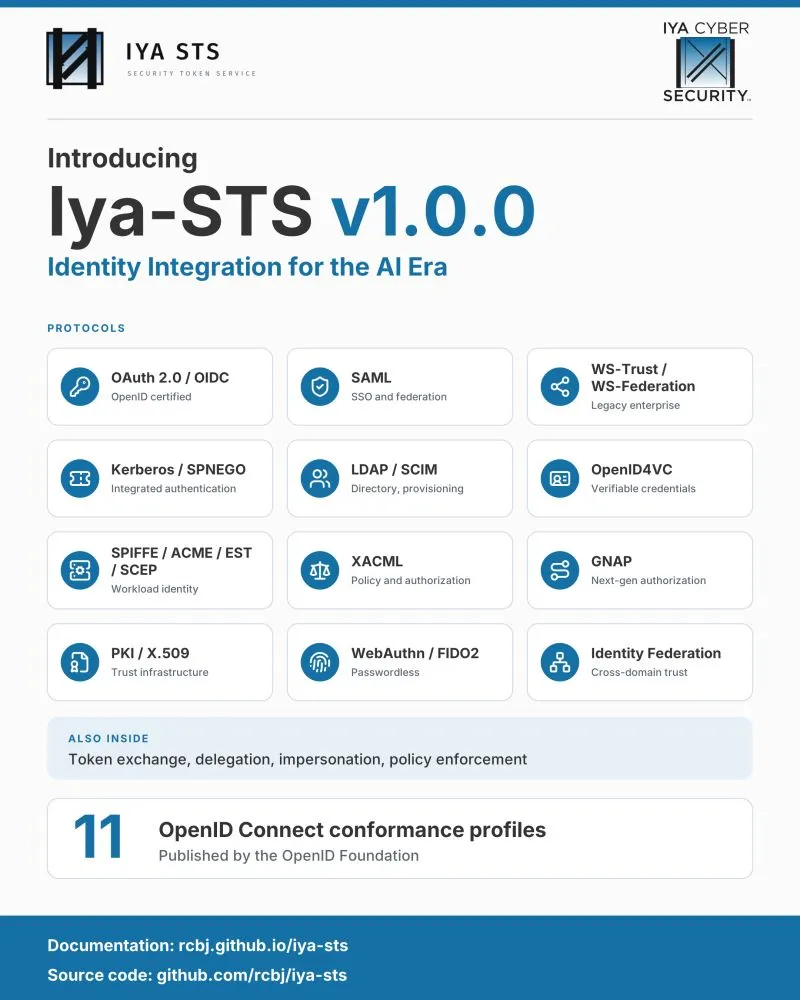
The full protocol list is in the graphic. More is planned.

Infographic introducing Iya-STS v1.0.0, Identity Integration for the AI Era. Twelve protocol areas: OAuth 2.0 / OIDC (OpenID certified), SAML (SSO and federation), WS-Trust / WS-Federation, Kerberos / SPNEGO, LDAP / SCIM, OpenID4VC, SPIFFE / ACME / EST / SCEP, XACML, GNAP, PKI / X.509, WebAuthn / FIDO2, and Identity Federation. Also inside: token exchange, delegation, impersonation, and policy enforcement. Eleven OpenID Connect conformance profiles, published by the OpenID Foundation.

Documentation · Source code